 ddos
ddos
313 Team Hits FBI NICS Site: 10-Hour Critical Outage Hits Federal Portal
> By Clara | Sep 01, 2026 | 3 min read
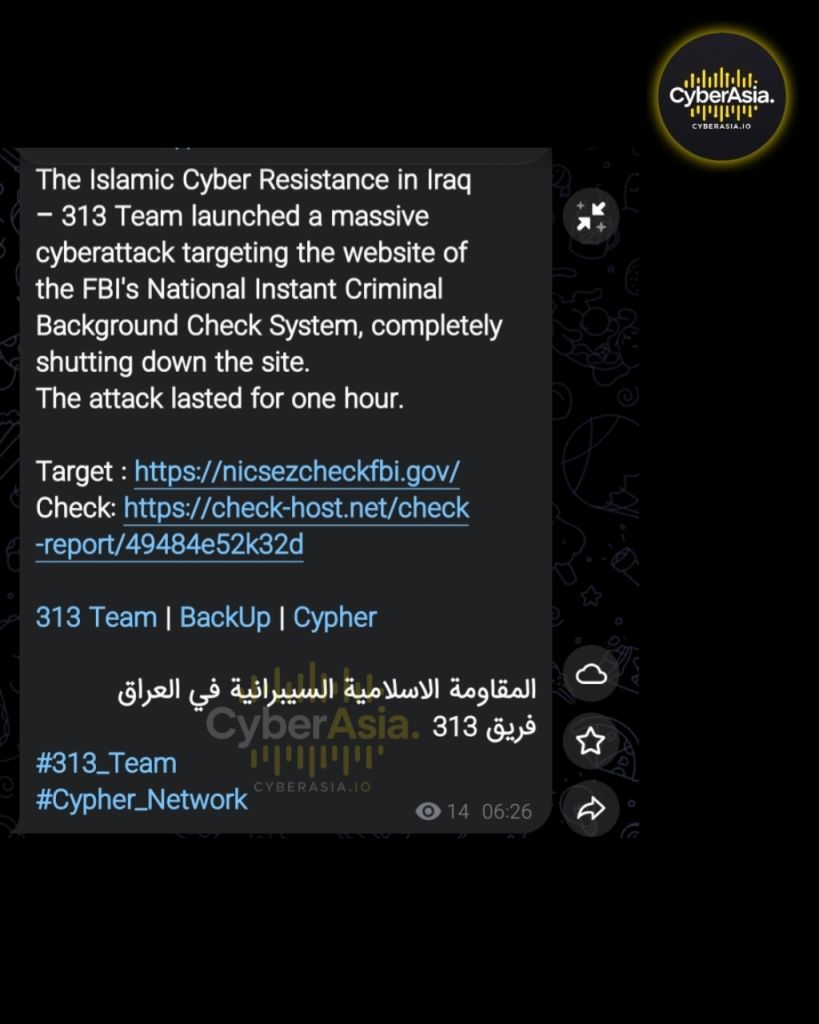
Iraqi hacktivist syndicate 313 Team has escalated its cyber offensive against United States federal infrastructure as the 313 Team hits FBI NICS site (nicsezcheckfbi.gov), inducing a 10-hour access blackout across the National Instant Criminal Background Check System portal.
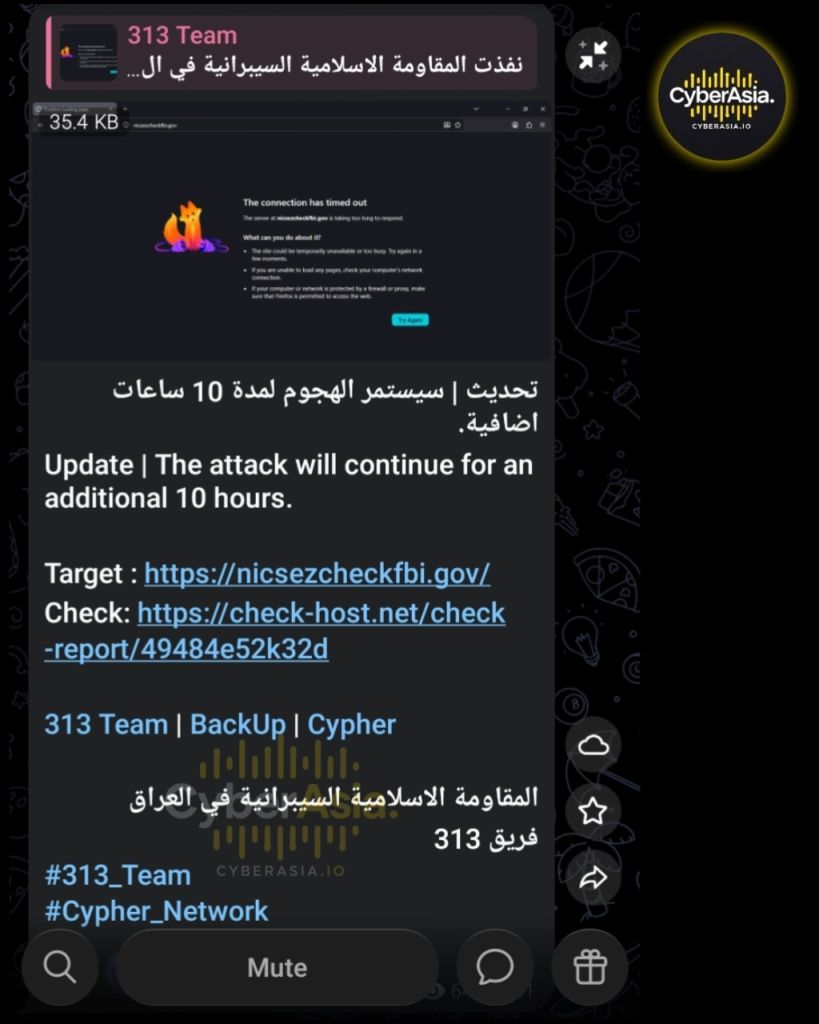
The operational claim surfaced across the collective’s official Telegram broadcast channel. Operating under the self-styled banner of the Islamic Cyber Resistance in Iraq, the group identified nicsezcheckfbi.gov as its primary objective. The targeted subdomain serves as the public electronic access point for the Federal Bureau of Investigation’s firearm background screening gateway.
Initial bulletins posted by the cell documented total server unresponsiveness within the first sixty minutes of the campaign. A subsequent status update confirmed that the operation had been extended to ten consecutive hours, accompanied by browser screenshots showing origin connection timeout errors when attempting to negotiate HTTP connections with the federal host.
Multi-Region Latency Diagnostics as 313 Team Hits FBI NICS Site
To substantiate the claimed service denial, the attackers released diagnostic telemetry recorded via independent monitoring platform Check-Host. Global probe nodes across more than fifty international test stations registered universal connection failure states.
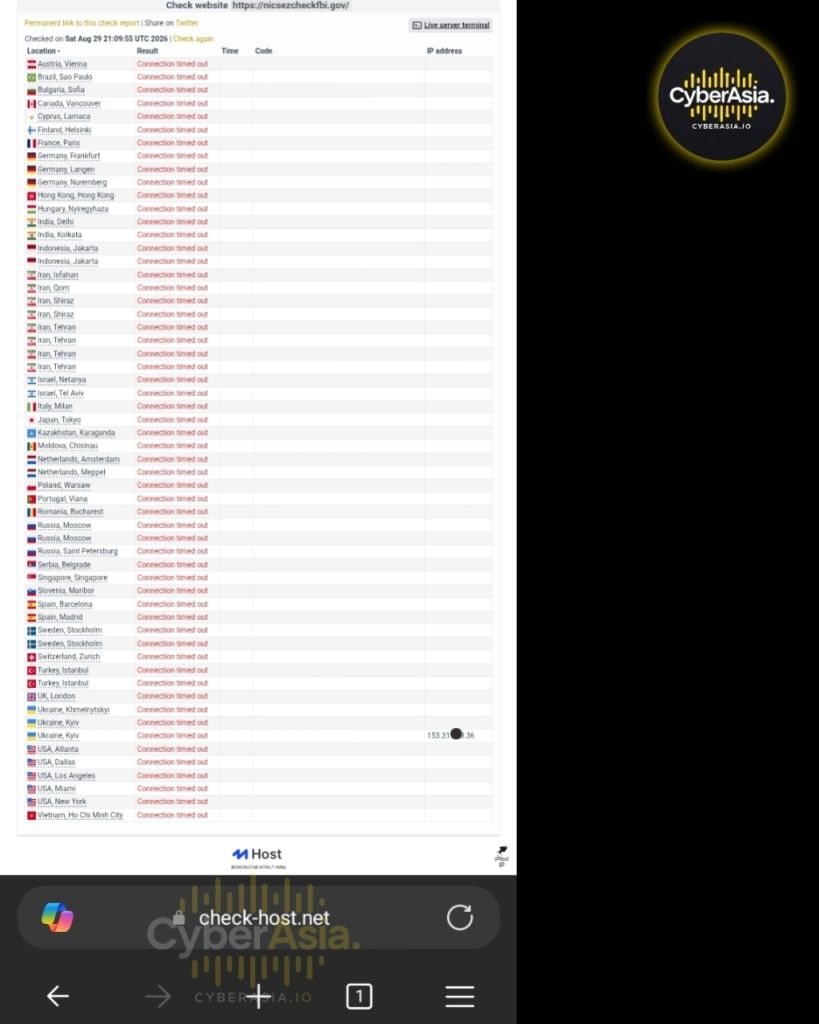
Monitoring nodes located across North America, Europe, and the Asia-Pacific (including Japan, Singapore, and India) uniformly logged “Connection timed out” errors. Public domain registry records indicate that nicsezcheckfbi.gov was registered in July 2000 to facilitate electronic firearm background checks by licensed gun dealers under federal statutory mandates.
Technical telemetry captured during the assault displayed origin resolution pointing toward IP range 153.31.xxx.36. The persistent timeout profile reflects application-layer socket exhaustion, wherein volumetric TCP connection floods deplete available worker threads on outward-facing web server daemons, preventing legitimate client handshakes.
Threat Actor Profile: 313 Team and the Iraqi Cyber Axis
313 Team operates as an Iraqi hacktivist collective aligned with regional paramilitary narratives. Operating under decentralized umbrellas including the Cypher Network and associated operational cells, the group regularly claims credit for transient denial-of-service strikes targeting Israeli and American federal digital assets.
Despite aggressive rhetorical framing on social channels, observed technical capabilities remain limited to commercial Layer 4 and Layer 7 stress testing frameworks. Rigorous forensic assessment confirms zero infiltration into backend criminal history repositories, zero database exfiltration, and zero lateral movement into secure Justice Department networks.
Operational Impact on Federal Firearms Verification
The National Instant Criminal Background Check System (NICS) serves as the primary verification engine mandated by federal statute to determine firearm purchase eligibility. Federal Firearms Licensees (FFLs) rely on electronic portals to verify criminal records, restraining orders, and disqualifying legal conditions.
While the strike temporarily disrupted the public nicsezcheckfbi.gov web interface, core law enforcement telecommunications links and telephonic verification lines remained isolated from public web traffic, mitigating disruption to nationwide background check operations.
Frequently Asked Questions
Q1: Was criminal background history or private citizen firearm registry data compromised?
No. Network telemetry verifies that the incident was strictly an external Layer 7 availability disruption against a front-facing web portal. The attackers achieved zero database penetration, and no law enforcement databases or civilian background records were compromised.
Q2: How did the attackers maintain a 10-hour disruption against a .gov web portal?
By leveraging distributed stresser bots routing requests through rotating proxies, the actors sustained high concurrency against origin web servers, exhausting connection pools. Without aggressive geo-filtering or behavioral rate-limiting, edge proxies pass connection attempts to the origin, causing sustained timeouts.
Q3: What engineering controls prevent denial of service on government authentication portals?
Federal agencies enforce multi-layered defense architectures including Anycast edge scrubbing networks, strict origin IP cloaking, cryptographic challenge barriers (such as CAPTCHA or Turnstile), and localized ASN rate limits to drop anomalous volumetric traffic before reaching internal web daemons.
This report is compiled strictly for cyber threat intelligence, defensive engineering, and educational research purposes based on verified open-source data and network telemetry. CyberAsia urges federal and enterprise network administrators to implement recommended edge mitigation protocols and never engage in unlawful network stress activities.
Disclaimer: The information presented in this threat intelligence report is for educational and cybersecurity research purposes only. CyberAsia reports on cyber incidents to help organizations understand and defend against emerging threats. We do not provide hacking instructions, host stolen data, or endorse illegal activities.
> INTELLIGENCE_NOTICE
The report above detailing 313 Team Hits FBI NICS Site: 10-Hour Critical Outage Hits Federal Portal is part of the CyberAsia public archive. For organizations requiring real-time attack telemetry, check-host latency records, and edge firewall mitigation strategies for ddos incidents, please refer to our Secure Drop or contact the research desk.


