 ddos
ddos
Israeli LGBTQ and Cyber Conference Sites Hit by Widespread Outages
> By Clara | Aug 04, 2026 | 4 min read
Israeli Websites Havruta, LGBT Olim & Cybertech Offline in Suspected RipperSec DDoS
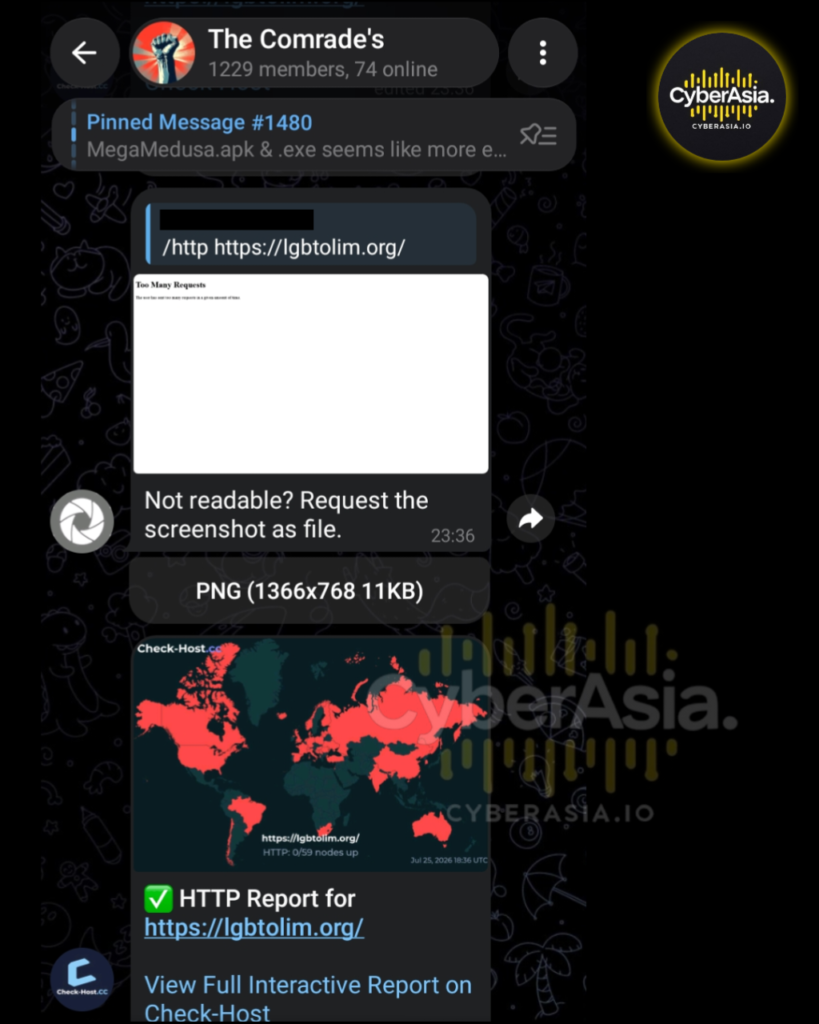
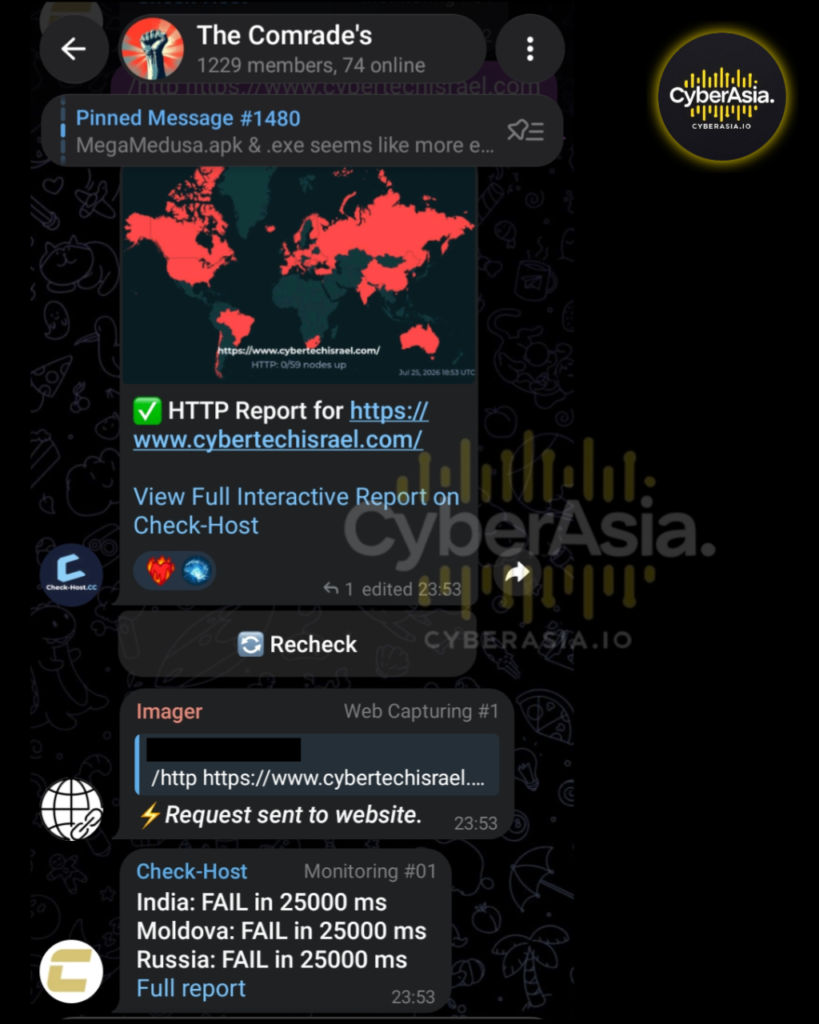
Several Israeli websites experienced significant accessibility problems on July 25, 2026, according to monitoring data shared in a Telegram channel linked to hacktivist activity. Screenshots posted in the channel The Comrade’s displayed Check-Host HTTP reports for three domains: havruta.org.il, lgbtolim.org, and www.cybertechisrael.com. The global node maps appeared predominantly red, indicating failed checks from the majority of testing locations.For havruta.org.il, the report showed only 6 out of 59 nodes up at the time of the check, with at least one result returning a 500 Internal Server Error. lgbtolim.org and cybertechisrael.com both registered 0 out of 59 nodes up. One capture for lgbtolim.org displayed a “Too Many Requests” error page.
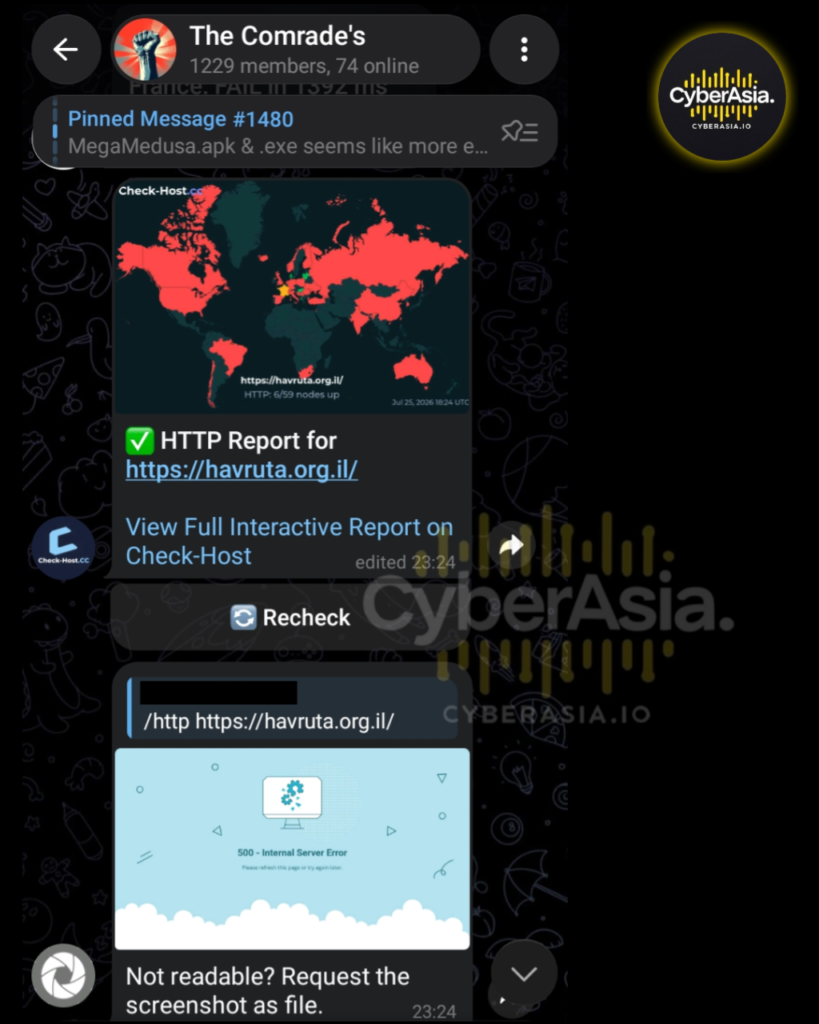
The channel’s pinned message referenced MegaMedusa.apk and .exe files. MegaMedusa is a DDoS tool previously linked to the pro-Palestinian hacktivist group RipperSec. The Comrade’s Group channel appears to serve as a platform for sharing monitoring results related to this activity.Havruta is an Israeli organization supporting religiously inclined Jewish LGBTQ individuals and promoting acceptance within Orthodox communities. LGBT Olim provides advocacy, information, and social support for LGBTQ Jews making Aliyah or already living in Israel. Cybertechisrael.com serves as the official site for Cybertech Global Tel Aviv, a major international cybersecurity conference and exhibition.
The outages were documented through public Check-Host results shared by The Comrade’s Group, rather than independent confirmation of a successful sustained attack. Website availability can fluctuate for many reasons, including technical issues, traffic spikes, or deliberate disruption. No official statements from the affected organizations regarding the July 25 incidents were immediately available at the time of reporting. Israeli organizations and websites have faced repeated DDoS campaigns from various hacktivist groups, particularly since October 2023. RipperSec has previously claimed responsibility for similar disruptions against Israeli targets, often using tools like MegaMedusa and publicizing results via Telegram channels, including those associated with The Comrade’s Group.
Organizations operating websites in geopolitically sensitive environments are advised to maintain robust DDoS protection, monitor traffic anomalies, and ensure backup communication channels remain available. Details on the duration and exact cause of these specific outages remain limited.
Verification Status
The 25 July 2026 cards for havruta.org.il, lgbtolim.org, and cybertechisrael.com come from Check-Host maps posted by The Comrade’s Group, with MegaMedusa binaries pinned in the same channel. CyberAsia did not run its own probes. Node maps can go red for rate-limits, hosting faults, or a flood. No organisation statement was on record at publication. Score this as a claimed multi-site disruption, not as a confirmed application breach or data theft.
Why These Three Domains Sit on the Same Card
Havruta and LGBT Olim are civil-society sites. Cybertech Global Tel Aviv is a commercial conference property. Grouping them on one Telegram card is a political signal, not proof of a shared hosting stack. MegaMedusa’s HTTP/2 flooder does not need a shared vulnerability. It needs DNS that resolves to an origin the operators can hammer. A conference site on a marketing CMS is as fragile as a small NGO on a single VPS.
Mitigation & Prevention Strategies
For the affected organisations / IT.
- Put a DDoS-capable edge in front of origin. The pinned MegaMedusa files are built for TLS request floods, not for SQLi.
- Separate the conference registration host from the brochure site so a homepage flood does not take ticket or donor payments down.
For attendees and community members.
- If a site is down, use the organisation’s official social account. Do not click “backup registration” links that appear in comments during the outage.
Analyst Note
Three unrelated organisations on one Telegram card is a narrative choice. Havruta, LGBT Olim, and a commercial conference site do not share a threat model. If you run any of them, measure your own origin 5xx rate. If you do not, do not amplify the card. MegaMedusa binaries in a pinned message tell you the intended technique, not whether it worked for twelve minutes or twelve hours.
What Would Upgrade This From a Claim
Origin 5xx logs from the three operators, a hosting-provider ticket, or a public statement. Check-Host redness plus a pinned MegaMedusa zip is below that bar. Civil-society sites and a conference brochure should not share an incident channel with each other in your SOC just because they shared a Telegram card. Measure each origin. Then decide if you even have an incident.
Disclaimer: The information presented in this threat intelligence report is for educational and cybersecurity research purposes only. CyberAsia reports on cyber incidents to help organizations understand and defend against emerging threats. We do not provide hacking instructions, host stolen data, or endorse illegal activities.
> INTELLIGENCE_NOTICE
The report above detailing Israeli LGBTQ and Cyber Conference Sites Hit by Widespread Outages is part of the CyberAsia public archive. For organizations requiring real-time attack telemetry, check-host latency records, and edge firewall mitigation strategies for ddos incidents, please refer to our Secure Drop or contact the research desk.


