 ddos
ddos
Pro-Russian Hacktivists “Dark Storm Team” Claim DDoS Hits on 3 Israeli Banks
> By Clara | Aug 04, 2026 | 3 min read
Cyberattacks / Hacktivism
Pro-Russian Hacktivists “Dark Storm Team” Claim DDoS Hits on 3 Israeli Banks
Pro-Russian hacktivist collective Dark Storm Team has claimed responsibility for distributed denial-of-service (DDoS) attacks against three Israeli financial institutions, posting alleged “check-host” outage reports on its Telegram channel as evidence.
What Happened
A hacktivist group calling itself Dark Storm Team has claimed a wave of distributed denial-of-service (DDoS) attacks targeting Israeli financial institutions, according to posts shared on the group’s Telegram channel.
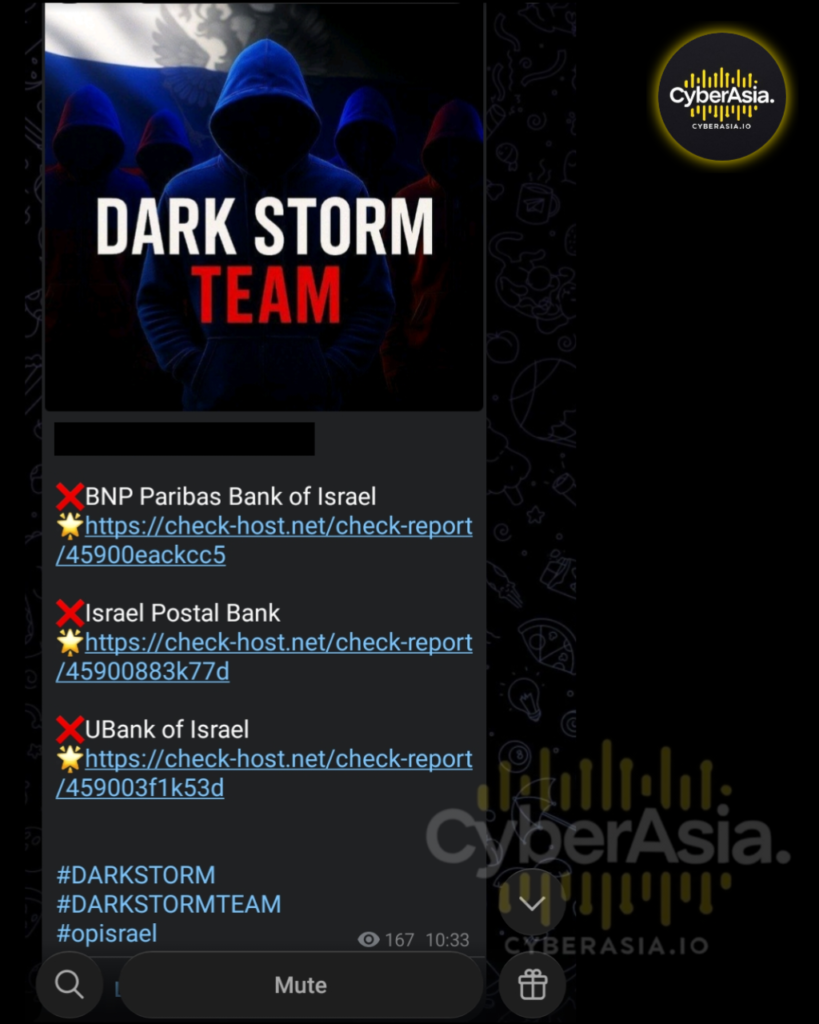
In messages published under the hashtags #DARKSTORM, #DARKSTORMTEAM, and #opisrael, the group listed three Israeli banking entities it says it disrupted:
> THREAT_INTELLIGENCE_DATA
- BNP Paribas Bank of Israel
- Israel Postal Bank
- UBank of Israel
Each entry was accompanied by a link to check-host.net, a third-party network monitoring service, which the group presented as proof that the targeted sites were experiencing connectivity issues at the time of posting. The post had reportedly drawn 167 views on the channel as of the time of writing.
Who Is Allegedly Affected
The claimed targets span multiple corners of Israel’s banking and financial-services sector, including a subsidiary of the French multinational bank BNP Paribas, a postal banking service, and a digital-only bank. No customer data theft, breach, or system compromise beyond service disruption has been claimed.
Technical Details
DDoS attacks work by flooding a target’s servers with overwhelming volumes of traffic, rendering websites or online services slow or unreachable for legitimate users. They typically do not involve data exfiltration or unauthorized system access. Check-host.net reports, of the kind cited by Dark Storm Team, show point-in-time reachability results from distributed probe nodes , they can indicate a site was briefly unreachable but are not independent confirmation of a sustained or attacker-caused outage.
Threat Actor Background
Dark Storm Team is a hacktivist collective that has previously claimed DDoS campaigns against government and infrastructure targets in various countries, often framing its activity around geopolitical causes. The visual branding in this post , hooded figures against a backdrop resembling the Russian flag , aligns with the group’s established pro-Russian, anti-Western messaging. The #opisrael tag references a long-running, loosely organized hacktivist campaign that periodically resurfaces around Israeli-Palestinian tensions, with various groups using it as an umbrella for opportunistic attacks.
Potential Impact
If accurate, brief service disruptions could temporarily affect online banking access for customers of the named institutions. DDoS incidents of this nature are generally short-lived and do not typically compromise core banking systems, transaction integrity, or customer data. However, they can cause reputational concern and operational strain on IT teams during the disruption window.
Response and Mitigation
This report is based solely on claims made by the threat actor and has not been independently verified. None of the named institutions , BNP Paribas Bank of Israel, Israel Postal Bank, or UBank of Israel , has publicly confirmed a service disruption at the time of writing. It remains unclear whether any outage occurred, how long it lasted, or whether it was attributable to a deliberate attack rather than routine network conditions.
Conclusion
Dark Storm Team’s latest claims fit a familiar pattern of hacktivist groups using low-cost DDoS attacks and self-reported “proof” screenshots to generate publicity around geopolitically motivated campaigns. Until the affected banks or independent researchers confirm the incidents, these claims should be treated as unverified. CyberAsia.io will update this report if official statements or further technical evidence emerge.
Mitigation & Prevention Strategies
To defend against advanced Layer 7 and volumetric DDoS attacks observed in these campaigns, organizations should implement the following defensive postures:
- Edge Protection: Deploy robust Web Application Firewalls (WAF) and Anti-DDoS solutions configured to challenge anomalous request rates (e.g., CAPTCHA or JS challenges) before they hit origin servers.
- Geographic Rate Limiting: If the threat actor originates from or utilizes botnets concentrated in specific regions, enforce geo-blocking rules for non-essential traffic.
- Infrastructure Scaling: Ensure load balancers and auto-scaling groups are optimized to absorb sudden traffic spikes while maintaining core service availability.
Disclaimer: The information presented in this threat intelligence report is for educational and cybersecurity research purposes only. CyberAsia reports on cyber incidents to help organizations understand and defend against emerging threats. We do not provide hacking instructions, host stolen data, or endorse illegal activities.
> INTELLIGENCE_NOTICE
The report above detailing Pro-Russian Hacktivists “Dark Storm Team” Claim DDoS Hits on 3 Israeli Banks is part of the CyberAsia public archive. For organizations requiring real-time attack telemetry, check-host latency records, and edge firewall mitigation strategies for ddos incidents, please refer to our Secure Drop or contact the research desk.


