 ddos
ddos
RipperSec DDoS Israel: National Tourism Portal Knocked Offline in #OpZionistV2
> By Clara | Aug 04, 2026 | 7 min read
:root{
, bg:#0a0a0a;
, panel:#131313;
, panel-border:#242424;
, text:#dcdcdc;
, text-dim:#8f8f8f;
, yellow:#f5c518;
, yellow-dim:#a88c1e;
, red:#e2493d;
}
*{box-sizing:border-box;}
html{scroll-behavior:smooth;}
body{
margin:0;
background:var(, bg);
color:var(, text);
font-family:’Inter’,system-ui,sans-serif;
line-height:1.7;
-webkit-font-smoothing:antialiased;
}
a{color:var(, yellow);text-decoration:none;}
a:hover{text-decoration:underline;}
a:focus-visible, button:focus-visible{outline:2px solid var(, yellow);outline-offset:2px;}
/* Masthead */
.masthead{
border-bottom:1px solid var(, panel-border);
padding:18px 24px;
display:flex;
align-items:center;
justify-content:space-between;
position:sticky;
top:0;
background:rgba(10,10,10,0.92);
backdrop-filter:blur(6px);
z-index:10;
}
.logo{
font-family:’Space Grotesk’,sans-serif;
font-weight:700;
font-size:20px;
color:var(, yellow);
letter-spacing:-0.02em;
}
.logo span{color:var(, text);}
.masthead-tag{
font-family:’IBM Plex Mono’,monospace;
font-size:11px;
color:var(, text-dim);
letter-spacing:0.08em;
text-transform:uppercase;
}
/* Article shell */
.wrap{max-width:760px;margin:0 auto;padding:48px 24px 96px;}
.eyebrow{
font-family:’IBM Plex Mono’,monospace;
font-size:12px;
letter-spacing:0.12em;
text-transform:uppercase;
color:var(, red);
display:flex;
align-items:center;
gap:8px;
margin-bottom:18px;
}
.eyebrow::before{
content:””;
width:7px;height:7px;border-radius:50%;
background:var(, red);
box-shadow:0 0 8px var(, red);
display:inline-block;
}
h1.headline{
font-family:’Space Grotesk’,sans-serif;
font-size:clamp(28px,4.4vw,42px);
font-weight:700;
line-height:1.15;
letter-spacing:-0.01em;
color:#fafafa;
margin:0 0 20px;
}
.meta-row{
display:flex;
flex-wrap:wrap;
gap:16px;
font-family:’IBM Plex Mono’,monospace;
font-size:12px;
color:var(, text-dim);
border-top:1px solid var(, panel-border);
border-bottom:1px solid var(, panel-border);
padding:14px 0;
margin-bottom:36px;
}
.meta-row b{color:var(, text);font-weight:500;}
.lede{
font-size:19px;
color:#f0f0f0;
font-weight:400;
margin-bottom:8px;
}
h2.sub{
font-family:’Space Grotesk’,sans-serif;
color:var(, yellow);
font-size:22px;
font-weight:600;
letter-spacing:-0.01em;
margin:44px 0 16px;
padding-bottom:8px;
border-bottom:1px solid var(, panel-border);
}
p{margin:0 0 18px;color:var(, text);}
strong{color:#fafafa;}
/* Terminal-style quote block for threat actor statements */
.terminal{
background:var(, panel);
border:1px solid var(, panel-border);
border-left:3px solid var(, yellow);
border-radius:6px;
padding:16px 18px;
margin:20px 0 26px;
font-family:’IBM Plex Mono’,monospace;
font-size:14px;
color:#f2f2f2;
}
.terminal .t-label{
color:var(, text-dim);
font-size:11px;
text-transform:uppercase;
letter-spacing:0.1em;
margin-bottom:10px;
display:flex;
align-items:center;
gap:8px;
}
.terminal .t-label::before{content:”$”;color:var(, yellow);}
.terminal .line{margin:0 0 4px;}
.terminal .line::before{content:”> “;color:var(, yellow-dim);}
/* Proof links */
.proof-box{
background:var(, panel);
border:1px solid var(, panel-border);
border-radius:6px;
padding:16px 18px;
margin:16px 0 28px;
}
.proof-box .p-title{
font-family:’IBM Plex Mono’,monospace;
font-size:11px;
color:var(, yellow);
text-transform:uppercase;
letter-spacing:0.1em;
margin-bottom:10px;
}
.proof-box ul{margin:0;padding:0;list-style:none;}
.proof-box li{
font-family:’IBM Plex Mono’,monospace;
font-size:12.5px;
padding:6px 0;
border-bottom:1px solid #1c1c1c;
word-break:break-all;
}
.proof-box li:last-child{border-bottom:none;}
ul.plain{padding-left:20px;margin:0 0 18px;}
ul.plain li{margin-bottom:8px;}
/* Disclaimer */
.disclaimer{
margin-top:48px;
padding:18px 20px;
background:#141008;
border:1px solid #3a2f10;
border-radius:6px;
}
.disclaimer .d-title{
font-family:’IBM Plex Mono’,monospace;
font-size:11px;
color:var(, yellow);
text-transform:uppercase;
letter-spacing:0.1em;
margin-bottom:8px;
}
.disclaimer p{color:var(, text-dim);font-size:13.5px;margin:0;}
/* Tags / footer meta */
.tags{
display:flex;
flex-wrap:wrap;
gap:8px;
margin-top:40px;
}
.tag{
font-family:’IBM Plex Mono’,monospace;
font-size:11px;
color:var(, yellow);
border:1px solid var(, yellow-dim);
border-radius:999px;
padding:5px 12px;
letter-spacing:0.03em;
}
footer{
border-top:1px solid var(, panel-border);
padding:28px 24px 60px;
text-align:center;
font-family:’IBM Plex Mono’,monospace;
font-size:11.5px;
color:var(, text-dim);
}
footer .logo{font-size:15px;}
@media (max-width:520px){
.wrap{padding:32px 18px 72px;}
h2.sub{font-size:19px;}
}
Pro-Palestinian hacktivist collectives RipperSec and The Comrade’s Group say they knocked Israel’s national tourism portal offline, framing the operation as the latest strike in an ongoing campaign against Israeli government and public-facing digital services.
What Happened
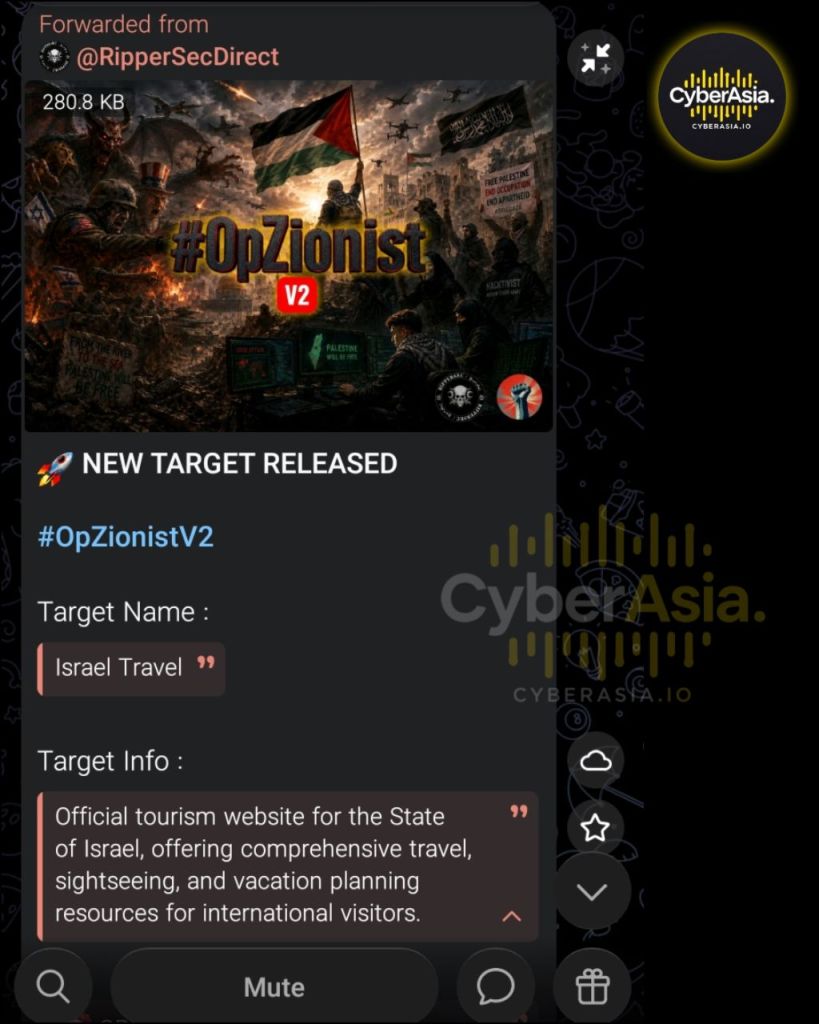
The two groups announced via their Telegram channel that they had targeted Israel Travel (israel.travel), the country’s official tourism website, with a Distributed Denial-of-Service (DDoS) operation. The action was billed as part of #OpZionistV2, a broader hacktivist push that has repeatedly zeroed in on Israeli state and public-sector web infrastructure in recent weeks.
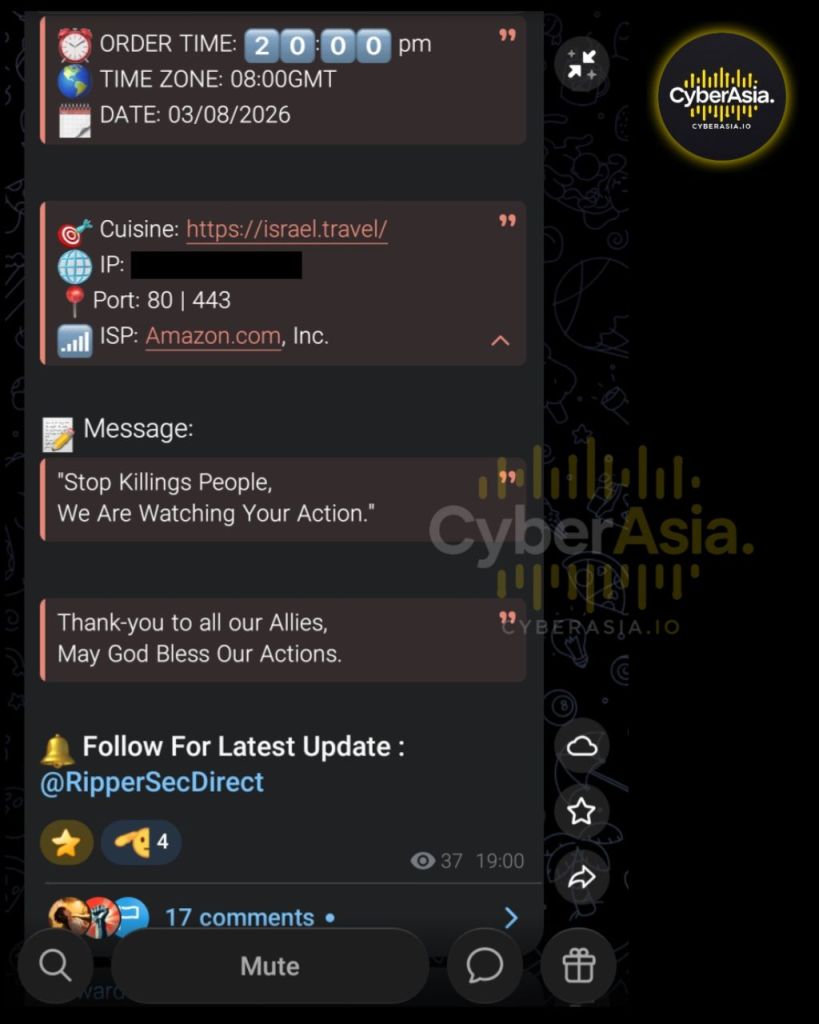
Per the group’s own posting , attributed to an account identified as RipperSecDirect , the strike was scheduled for August 3, 2026, at 20:00 GMT+8. The site was described by the attackers as Israel’s primary tourism hub, used to promote travel guidance, sightseeing itineraries, and vacation planning for international visitors.
Who’s Behind It
RipperSec and The Comrade’s Group are among several pro-Palestinian hacktivist entities that have banded together under the #OpZionistV2 banner. Their public messaging leans heavily on symbolic, ideologically framed statements rather than technical disclosure.
Telegram Announcement
“Stop Killings People, We Are Watching Your Action.”
“Thank-you to all our Allies, May God Bless Our Actions.”
These statements have not been independently verified beyond their appearance on the group’s own channel, and CyberAsia is reporting them strictly as claims made by the threat actors.
Who’s Affected
The claimed target is a public-facing, government-operated tourism platform rather than internal or customer-data systems. Sites of this kind are frequently chosen by hacktivist groups during periods of geopolitical tension because a visible outage generates media coverage and amplifies a campaign’s messaging without requiring advanced intrusion skills.
Verification Status
CyberAsia has not independently confirmed that the reported disruption was caused exclusively by a DDoS attack from RipperSec and The Comrade’s Group. Attribution in hacktivist incidents is notoriously hard to pin down without technical telemetry from the targeted organization or an independent incident response team.
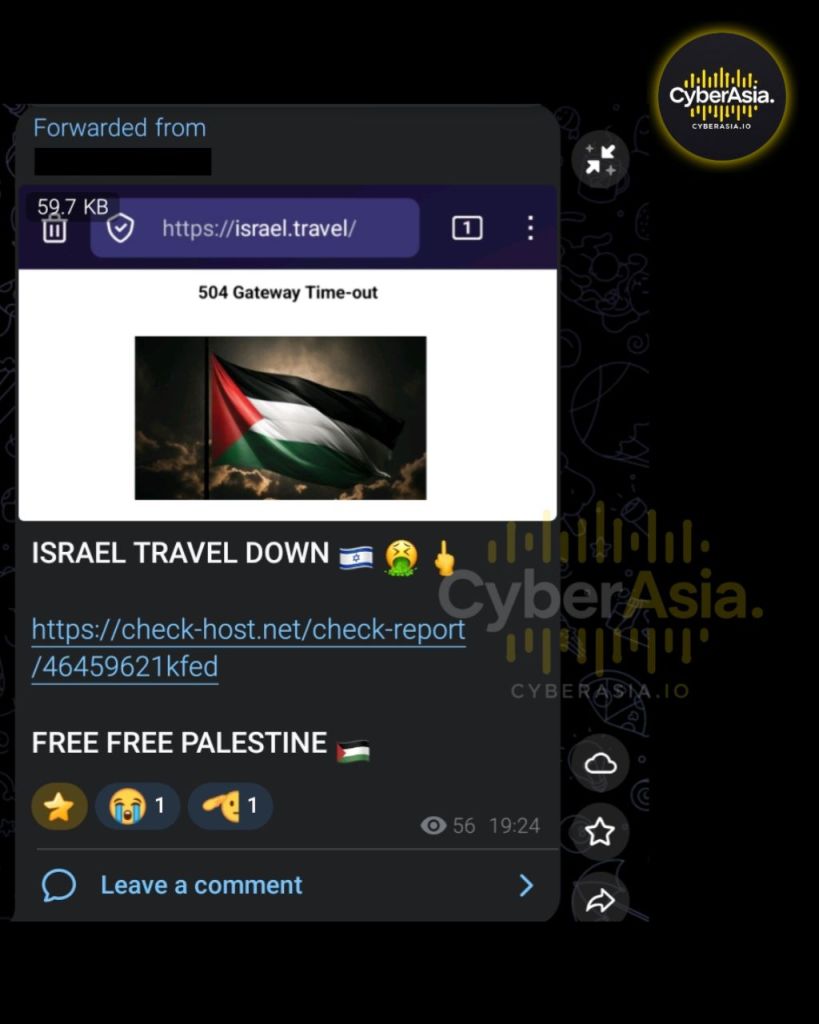
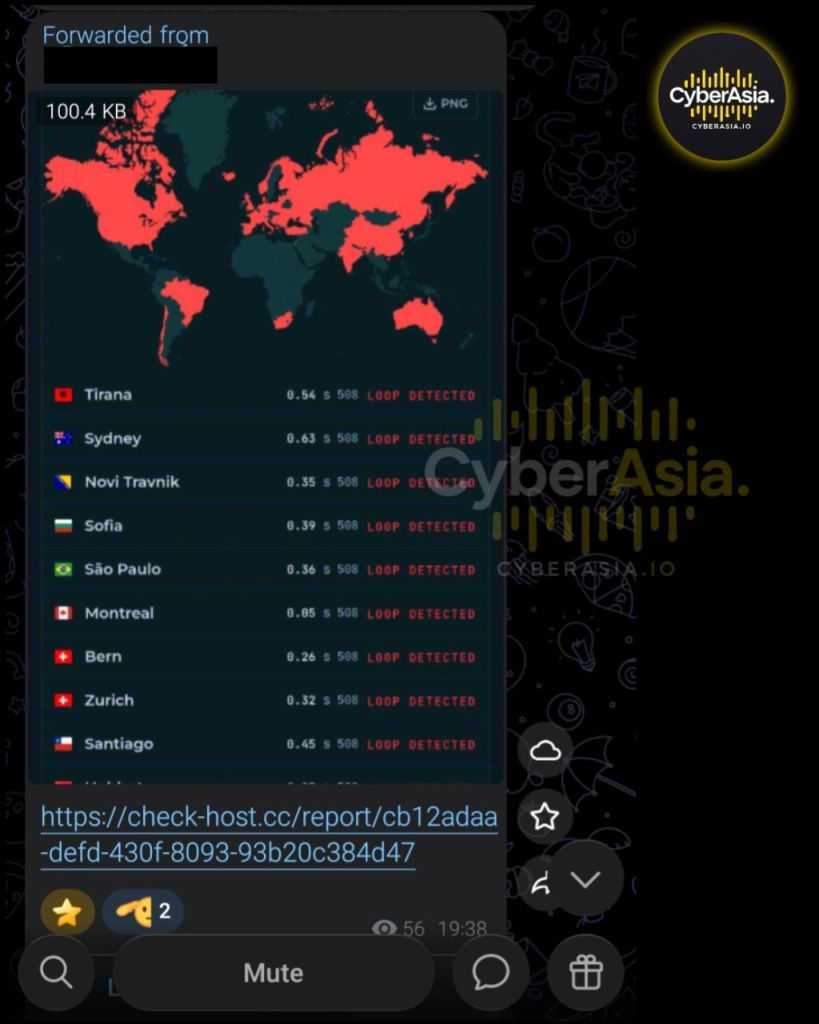
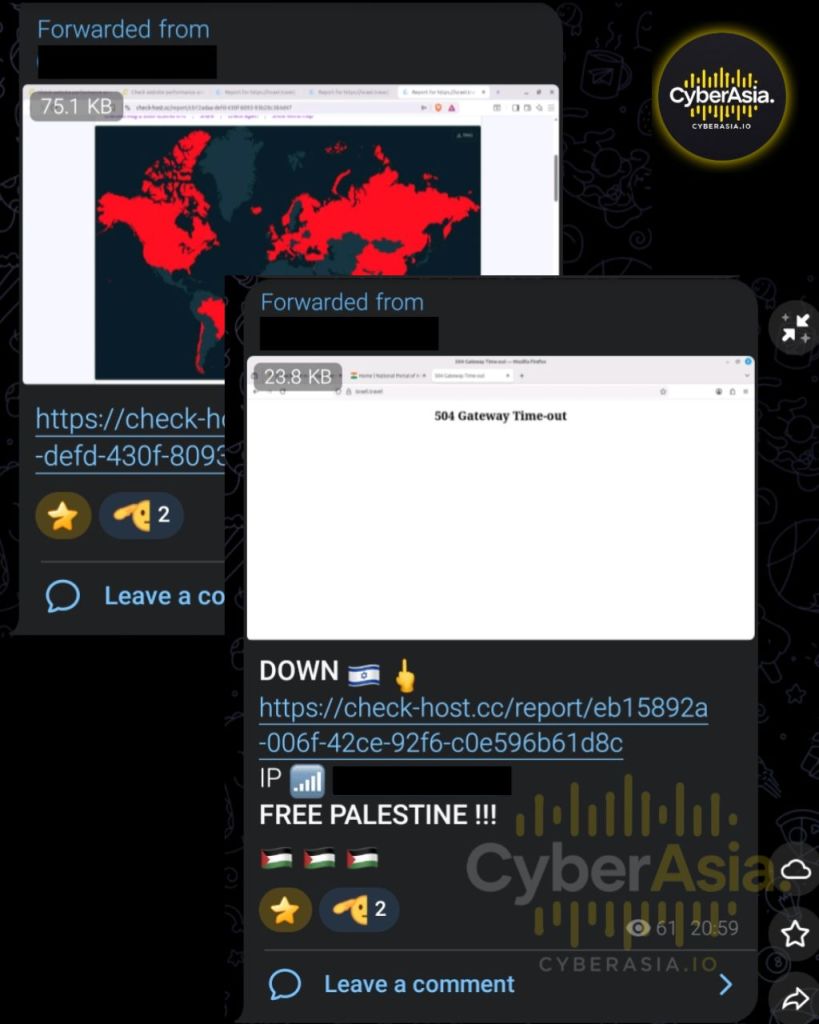
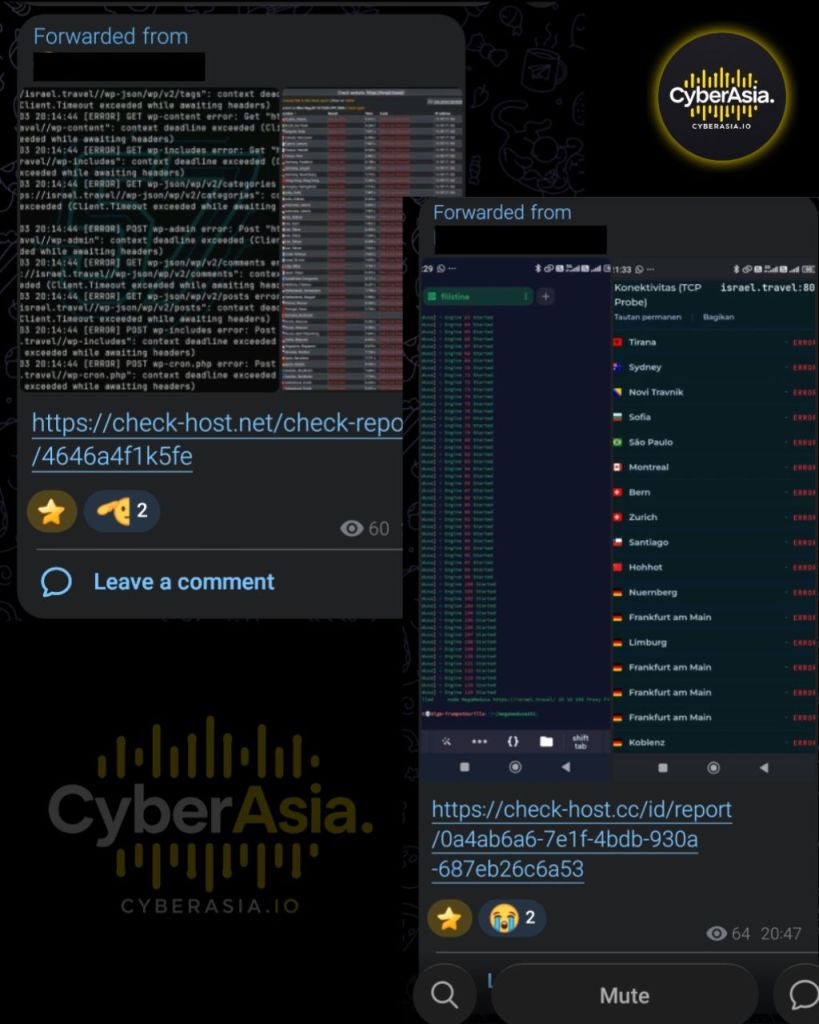
That said, several publicly circulated Check-Host monitoring snapshots tied to the claimed operation show the target domain returning periods of unavailability from multiple global checkpoints around the stated attack window. This is corroborating evidence of an outage , it does not, on its own, prove the cause.
Check-Host Monitoring Reports (as shared by threat actors)
> THREAT_INTELLIGENCE_DATA
- https://check-host.net/check-report/46459621kfed
- https://check-host.cc/report/cb12adaa-defd-430f-8093-93b20c384d47
- https://check-host.cc/report/eb15892a-006f-42ce-92f6-c0e596b61d8c
- https://check-host.net/check-report/4646a4f1k5fe
- https://check-host.cc/id/report/0a4ab6a6-7e1f-4bdb-930a-687eb26c6a53
Technical Background: How DDoS Attacks Work
A DDoS attack floods a target service with traffic from many sources at once, exhausting bandwidth or server resources until legitimate visitors can no longer connect. Unlike a data breach, a successful DDoS operation does not by itself indicate that attackers gained access to backend systems, databases, or customer records , its impact is typically limited to temporary availability loss.
#OpZionistV2, as promoted across multiple pro-Palestinian hacktivist groups, has so far centered on this kind of disruption-focused activity rather than deeper network intrusion or data theft.
Potential Impact
> COMPROMISED_DATA_RECORDS
- Temporary loss of access to travel information and booking-adjacent resources for international visitors.
- Reputational and symbolic impact tied to a visible, publicly reported outage.
- No confirmed evidence, at this stage, of a backend compromise or data exposure.
Recommended Mitigations
Organizations running public-facing government or tourism platforms are encouraged to:
- Deploy layered DDoS protection across network and application layers.
- Route traffic through a content delivery network (CDN) to absorb volumetric spikes.
- Implement traffic filtering and rate limiting at the edge.
- Continuously monitor for abnormal traffic patterns to enable early detection and response.
What’s Next
CyberAsia will continue tracking developments tied to the #OpZionistV2 campaign and will update this report if the affected organization issues an official statement or if independent technical evidence emerges confirming the cause of the outage.
Editorial Disclaimer
This article reports claims made by the named threat actors alongside publicly shared availability-monitoring data. The reported outage should not be treated as definitive proof that RipperSec or The Comrade’s Group caused the disruption unless confirmed through independent technical investigation or an official statement from the affected organization.
Mitigation & Prevention Strategies
To defend against advanced Layer 7 and volumetric DDoS attacks observed in these campaigns, organizations should implement the following defensive postures:
- Edge Protection: Deploy robust Web Application Firewalls (WAF) and Anti-DDoS solutions configured to challenge anomalous request rates (e.g., CAPTCHA or JS challenges) before they hit origin servers.
- Geographic Rate Limiting: If the threat actor originates from or utilizes botnets concentrated in specific regions, enforce geo-blocking rules for non-essential traffic.
- Infrastructure Scaling: Ensure load balancers and auto-scaling groups are optimized to absorb sudden traffic spikes while maintaining core service availability.
Disclaimer: The information presented in this threat intelligence report is for educational and cybersecurity research purposes only. CyberAsia reports on cyber incidents to help organizations understand and defend against emerging threats. We do not provide hacking instructions, host stolen data, or endorse illegal activities.
> INTELLIGENCE_NOTICE
The report above detailing RipperSec DDoS Israel: National Tourism Portal Knocked Offline in #OpZionistV2 is part of the CyberAsia public archive. For organizations requiring real-time attack telemetry, check-host latency records, and edge firewall mitigation strategies for ddos incidents, please refer to our Secure Drop or contact the research desk.


