scada
scada
Operation Barracuda: RipperSec Compromises Swedish SCADA Network Over Chat Control
> By Haider | Aug 11, 2026 | 4 min read
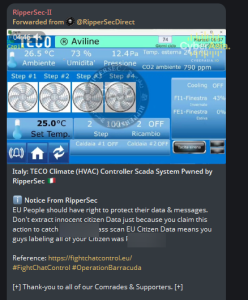
The hacktivist collective known as RipperSec has claimed responsibility for breaching a critical Swedish SCADA network. Operating under the campaign banner of #OperationBarracuda, the group published a screenshot demonstrating full administrative access to the SCADA (Supervisory Control and Data Acquisition) interface of Industri & Laboratoriekyl, a Swedish firm specializing in industrial and laboratory cooling solutions.
The breach appears to be politically motivated, aimed directly at the European Union’s controversial “Chat Control” legislation. In their release notes, RipperSec explicitly protested the EU’s push for mass scanning of citizen messages, stating that the action wrongly labels citizens as predators under the guise of child protection.
Technical Analysis: Swedish SCADA Network Exposure
The exfiltrated screenshot reveals a live SCADA HMI (Human-Machine Interface) controlling the thermal regulation systems of an unknown facility. The interface displays active real-time metrics, including temperature nodes, pressure valves (VP1, VP2), and cooling tanks (ACK Tank, VVB-Slingtank). The timestamp on the interface confirms the breach occurred recently, indicating an active session.
> TARGET_INFRASTRUCTURE: INDUSTRI_LABORATORIEKYL
- System Type: SCADA / ICS (Human-Machine Interface)
- Compromised Nodes: Cooling tanks, pressure pumps, and temperature sensors
- Location: Sweden (EU)
- Actor Motivation: Political protest against EU Chat Control legislation ([REDACTED])
Internet-facing SCADA systems remain a chronic vulnerability across global infrastructure. Attackers frequently utilize tools like Shodan or Censys to discover unauthenticated or default-credentialed VNC (Virtual Network Computing) instances and web panels controlling physical hardware. A malicious actor with this level of access could theoretically manipulate temperature thresholds, potentially destroying temperature-sensitive biological samples, pharmaceuticals, or industrial materials stored in the affected facility.

Mitigation Recommendations
For ICS/OT Administrators and Infrastructure Providers:
- Disconnect HMIs from the public internet. Ensure that no SCADA interface, VNC server, or OT (Operational Technology) dashboard is directly accessible from the WAN. Force all remote access through a secure, heavily monitored VPN with hardware MFA.
- Segment OT and IT networks. Implement strict network segmentation (the Purdue Model) to ensure that a breach in the corporate IT environment or a third-party vendor network cannot pivot into the physical control systems.
- Audit default credentials. ICS hardware is notorious for shipping with hardcoded or default passwords. Conduct an immediate audit of all PLCs (Programmable Logic Controllers) and HMIs to ensure default access has been disabled or rotated.
- Monitor for anomalies. Deploy OT-specific network monitoring tools to detect unauthorized commands sent to PLCs, such as unexpected setpoint changes or firmware overwrite attempts.
For the general public and EU citizens:
- Understand that while hacktivist attacks highlight political issues, any disruption to laboratory or industrial cooling systems could impact the supply chain of medical or essential goods in your region.
- Rely on official statements from local authorities regarding the safety and integrity of national infrastructure, rather than claims made on Telegram channels.
> DISCLAIMER
The information provided in this article is for educational and threat intelligence purposes only. CyberAsia does not condone, promote, or encourage any illegal activities, including data breaches or unauthorized access to systems. The claims made by threat actors are unverified and reported strictly for awareness and defensive mitigation.
> subscribe_to_intel
Join 5,000+ analysts. Get uncensored threat intelligence and breach alerts delivered directly to your inbox. Privacy Policy.
Mitigation & Prevention Strategies
Exploitation of vulnerabilities in critical infrastructure and edge devices requires immediate remediation to prevent catastrophic disruption:
- Patch Management: Apply vendor-supplied security patches or firmware updates immediately. For legacy systems, deploy virtual patching via network firewalls.
- Isolate OT Networks: SCADA and OT environments must be strictly isolated from corporate IT networks (the Purdue Model) to prevent spillover attacks.
- Continuous Monitoring: Deploy Endpoint Detection and Response (EDR) solutions and monitor network traffic for indicators of compromise (IoCs) associated with known exploits.
Strategic Defense Matrix and Incident Hardening
Operational intelligence analysis of this scada campaign indicates that the threat actors frequently exploit configuration oversights, unpatched external-facing gateways, and weak credential management policies across targeted organizations. Enterprise security operations centers (SOC) and defensive engineering teams must deploy layered perimeter safeguards to detect and neutralize similar threat vectors before lateral movement occurs.
- Continuous Asset and Perimeter Auditing: Maintain real-time inventory of all public-facing services, verifying SSL/TLS certificates and eliminating unauthenticated administrative interfaces following CISA Defensive Guidelines.
- Behavioral Anomaly and Zero-Trust Telemetry: Enforce strict hardware-backed multi-factor authentication (MFA) across all remote access nodes and implement endpoint detection and response (EDR) telemetry mapped to the MITRE ATT&CK Framework.
- Threat Intelligence Integration: Security teams are encouraged to correlate emerging indicators of compromise (IoCs) and evaluate network vulnerability profiles using our Cyber Risk Checker or submit anonymous confidential threat data via CyberAsia Secure Drop.
Disclaimer: The information presented in this threat intelligence report is for educational and cybersecurity research purposes only. CyberAsia reports on cyber incidents to help organizations understand and defend against emerging threats. We do not provide hacking instructions, host stolen data, or endorse illegal activities.
> INTELLIGENCE_NOTICE
The report above detailing Operation Barracuda: RipperSec Compromises Swedish SCADA Network Over Chat Control is part of the CyberAsia public archive. For organizations requiring Indicators of Compromise (IoCs), YARA signatures, and specialized malware containment guidelines for scada threats, please refer to our Secure Drop or contact the research desk.