 Threat Intelligence
~/ › Threat Intelligence › article
Threat Intelligence
CyberTroopers: 5 Dangerous Ways Politicians Manipulate Voters Online
> By Haider | Aug 31, 2026 | 8 min read
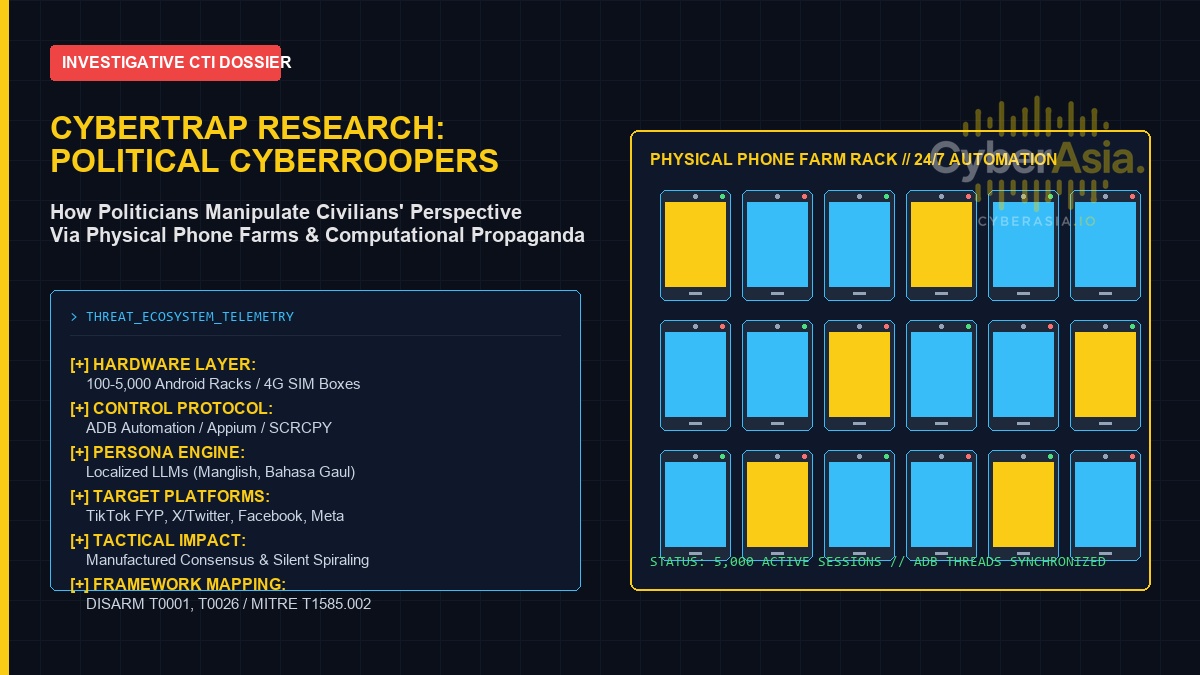
CyberTroopers have evolved from rudimentary troll armies into highly industrialized computational propaganda syndicates that fundamentally distort democratic discourse. Operating at the intersection of mobile automation, psychological conditioning, and algorithm exploitation, these specialized digital units execute coordinated cognitive warfare campaigns commissioned by political operatives. Instead of relying on isolated human commentators, modern political strategists deploy state-of-the-art CyberTroopers supported by physical phone farms and localized artificial intelligence to engineer manufactured consensus across social media feeds.
> TABLE_OF_CONTENTS [toggle]
- > The Hardware Ecosystem Behind Modern CyberTroopers
- > The 3-Phase Account Maturation and LLM Persona Funnel
- > 5 Dangerous Cognitive Warfare Tactics Used by CyberTroopers
- > DISARM and MITRE ATT&CK Threat Actor Mapping
- > Actionable Defense: Detecting Synthetic Inauthentic Networks
- > Frequently Asked Questions
The Hardware Ecosystem Behind Modern CyberTroopers
Public understanding of digital influence operations often assumes that fake engagement is generated by virtual software emulators or simple cloud-based bot scripts. However, defensive algorithms deployed by platforms such as TikTok, X (formerly Twitter), and Meta have rendered virtualized emulators largely obsolete. In response, modern CyberTroopers have transitioned to physical phone farm hardware ecosystems.
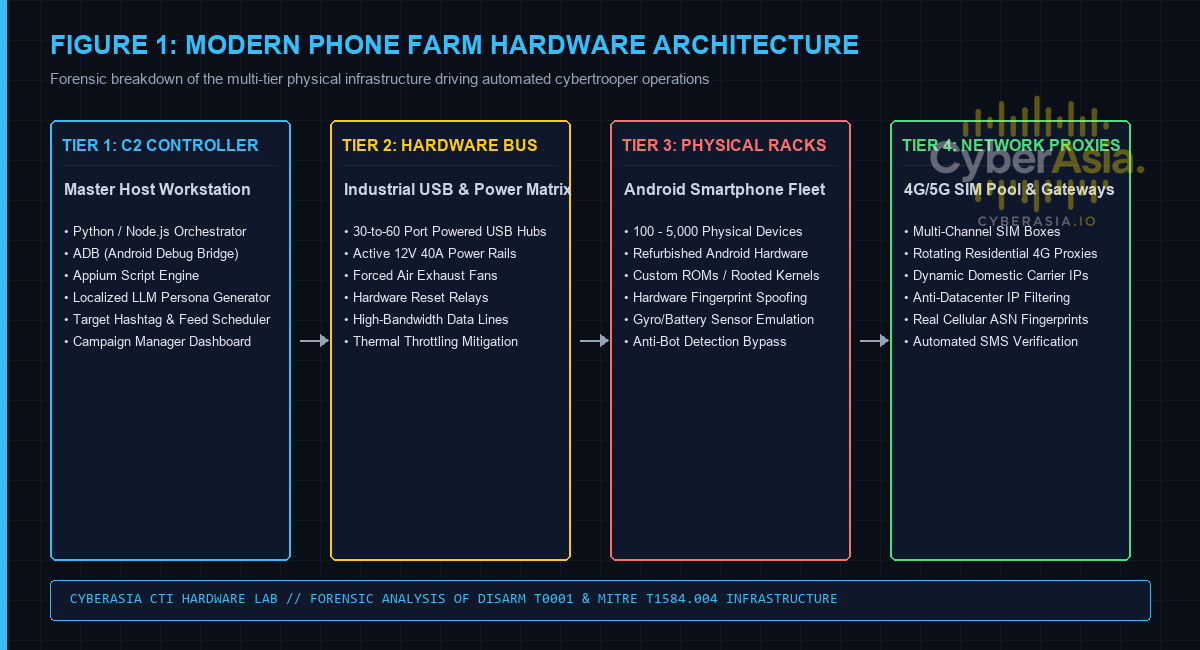
A physical phone farm consists of hundreds to thousands of stripped Android smartphones mounted vertically on custom server racks with active forced-air cooling. By operating on genuine physical silicon, each device generates authentic hardware telemetry, including valid IMEI numbers, unique GPU shaders, physical battery temperature curves, and authentic accelerometer noise. When social platforms inspect client-side device integrity, phone farm devices pass fraud checks with flawless trust scores, allowing CyberTroopers to maintain thousands of unflagged operational accounts.
In Southeast Asia and regional political theaters, dedicated computational propaganda agencies maintain secretive warehouses packed with multi-device racks. These specialized CyberTroopers interface with industrial multi-port USB matrix controllers that link directly into master command-and-control workstations, automating thousands of simultaneous interactions with zero human lag.
> PHONE_FARM_TECHNICAL_ARCHITECTURE
- C2 Orchestration: Central master workstations communicate via
ADB (Android Debug Bridge), SCRCPY, and Appium automation frameworks. - Human Touch Emulation: Scripts simulate randomized bezier curve swipes, human typing jitter, and variable latency pauses to bypass behavioral anomaly filters.
- 4G/5G Cellular Proxy Gateways: Devices route traffic through multi-channel SIM boxes with domestic carrier SIM cards, avoiding flagged datacenter IP ranges.
- Multi-Tenant Operation: A single handler team of 3 to 5 operators can seamlessly orchestrate over 5,000 synchronized accounts simultaneously.
The 3-Phase Account Maturation and LLM Persona Funnel
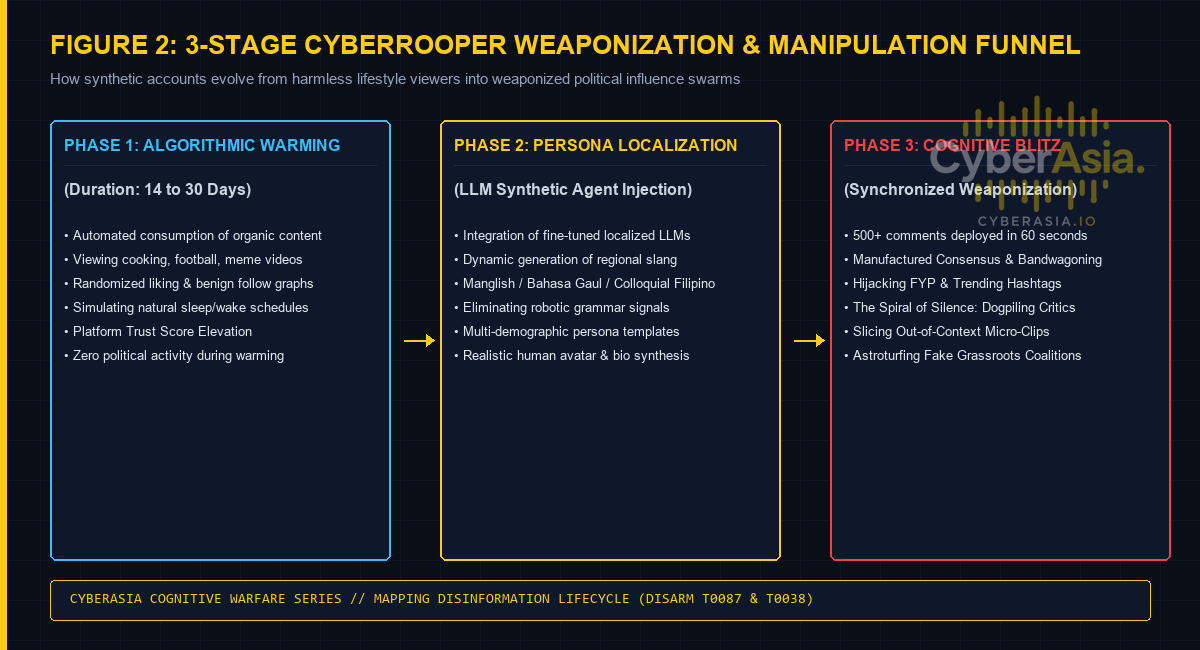
Professional political campaigns do not deploy freshly created accounts directly into controversial political arguments. Platforms enforce strict “sandbox” restrictions on newly registered handles. To maximize operational longevity, CyberTroopers utilize a disciplined 3-phase account maturation pipeline before weaponization.
During the initial Algorithmic Warming Phase, synthetic accounts spend 14 to 30 days consuming completely non-political content. Automated scripts browse cooking videos, football highlights, meme compilations, and local tourism posts. The accounts leave generic positive reactions, simulate human sleep schedules by going dormant at night, and follow established lifestyle creators to accumulate high platform reputation scores.
[TACTICAL INSIGHT] “By combining aged mobile device fingerprints with localized Large Language Models fine-tuned on regional dialects like Manglish and Bahasa Gaul, political operators eliminate the broken grammar tells that previously exposed bot swarms.”
Once warmed, accounts enter the Persona Localization Phase. Rather than using repetitive copy-pasted text, handlers integrate specialized Large Language Model (LLM) agents. These synthetic personas generate nuanced, localized commentary incorporating regional slang, cultural metaphors, and deliberate minor typos, ensuring every comment in a 500-bot swarm deployed by CyberTroopers appears completely distinct and human-authored.
In the final weaponization phase, handlers organize their automated accounts into specialized operational clusters. Certain nodes act as “cheerleaders” that praise political figures, while auxiliary shock-troops coordinate character assassination strikes against political opponents.
5 Dangerous Cognitive Warfare Tactics Used by CyberTroopers
When political elections or policy crises unfold, handlers transition their warmed fleets into active cognitive warfare operations. Modern CyberTroopers deploy 5 primary strategic vectors designed to manipulate civilian psychology and distort election outcomes:
1. Manufactured Consensus and the Bandwagon Effect. Human psychology is deeply vulnerable to perceived social consensus. When a voter sees a speech or policy proposal accompanied by 1,000 enthusiastic comments within the first 3 minutes of publication, the psychological “Bandwagon Effect” leads them to conclude that the majority of citizens support the position. CyberTroopers engineer this artificial consensus on demand, normalizing radical policies and creating the illusion of overwhelming grassroots popularity.
2. Algorithmic Hijacking and Trend Seeding. Social media recommendation algorithms prioritize early velocity of engagement (likes, shares, and rapid comment threads). CyberTrooper swarms deploy synchronized blitzes against selected hashtags or video uploads during the crucial first 15 minutes of release. This artificial momentum triggers algorithmic promotion, forcing political propaganda onto the “For You Pages” (FYP) and trending sidebars of hundreds of thousands of neutral, undecided voters who are completely unaware that CyberTroopers orchestrated the surge.
3. The Spiral of Silence and Coordinated Brigading. When independent journalists, civil society advocates, or opposition figures publish critical investigations, CyberTroopers initiate aggressive brigading campaigns. Hundreds of synthetic accounts flood the critic’s profile with synchronized mockery, personal insults, and false reports to trigger automated platform bans. This tactical harassment induces the psychological “Spiral of Silence,” intimidating everyday citizens into self-censorship out of fear of public backlash.
4. Decontextualized Micro-Clips and Emotional Outrage Triggers. CyberTrooper content factories slice 3-to-5 second out-of-context video snippets from political debates or interviews. By stripping away crucial context and pairing the clip with provocative audio tracks and misleading on-screen captions, operators trigger visceral emotional reactions such as anger or fear. Because emotional outrage spreads 6 times faster than factual corrections on social algorithms, CyberTroopers achieve irreversible psychological impact before fact-checkers can intervene.
5. Astroturfing Synthetic Grassroots Coalitions. Operators manufacture entire “paper movements” that mimic authentic citizen organizations. These synthetic coalitions create branded Facebook groups, TikTok channels, and X spaces featuring professionally designed 3D logos, custom banners, and automated memberships. Trained CyberTroopers publish joint declarations of support for political candidates, masquerading as legitimate youth movements, religious coalitions, or consumer advocacy groups to deceive news outlets and the voting public.
DISARM and MITRE ATT&CK Threat Actor Mapping
To systematically categorize computational propaganda, threat intelligence researchers map influence operations against established cybersecurity frameworks, including the DISARM Framework and MITRE ATT&CK for Enterprise. Similar to previous CyberAsia investigations into coordinated cyber syndicates, tracking adversary infrastructure deployed by CyberTroopers reveals structural patterns of digital cognitive aggression.
> THREAT_FRAMEWORK_MAPPING_MATRIX
DISARM T0001Create Inauthentic Accounts: Mass generation of synthetic mobile social media profiles managed by CyberTroopers via phone farm hardware.DISARM T0026Flood Information Space: Deploying multi-threaded comment blitzes to drown out legitimate dissent and organic reporting.DISARM T0087Manufacture Inauthentic Engagement: Artificially inflating likes, shares, and algorithmic velocity through automated scripts.MITRE T1585.002Establish Social Media Accounts: Maintaining active social media operational rosters for narrative deployment.MITRE T1584.004Server & Mobile Infrastructure: Maintaining proxy pools, SIM boxes, and dedicated C2 workstations for active CyberTroopers.
Actionable Defense: Detecting Synthetic Inauthentic Networks
Countering state-sponsored and political computational propaganda requires multi-layered vigilance from both platform integrity engineers and everyday digital citizens contending with sophisticated CyberTroopers:
For Digital Citizens & Journalists:
- Audit Interaction Velocity: Beware of comment sections where dozens of accounts post identically themed arguments within seconds of a post being published. Authentic human engagement follows organic Poisson distribution curves, not synchronized spikes orchestrated by CyberTroopers.
- Inspect Account Posting Timelines: Examine profiles leading aggressive brigading campaigns. Synthetic accounts often exhibit months of generic lifestyle content followed by a sudden, abrupt shift to 100% partisan political messaging.
- Verify Full Video Sources: Never share provocative 3-second micro-clips without locating and verifying the uncut, primary source video to understand the full context.
For Platform Integrity & Security Teams:
- Cellular Subnet Clustering Analysis: Analyze burst traffic originating from specific 4G/5G residential IP subnets exhibiting synchronized API requests across multiple distinct user identifiers.
- Touch Geometry Heuristics: Implement machine learning models to detect repetitive touch coordinate vectors and unnatural touch pressure distributions generated by ADB screen emulation.
- Coordinated Inauthentic Behavior (CIB) Graphing: Deploy graph neural networks to identify dense clusters of accounts that repeatedly amplify the same niche political domains across disparate social graphs.
Frequently Asked Questions
Q1: What is the difference between a traditional botnet and a physical phone farm?
Traditional botnets rely on virtual emulators or compromised IoT devices running headless browser scripts, which modern social platforms detect through canvas fingerprinting and missing hardware sensor data. Physical phone farms used by CyberTroopers deploy actual Android hardware and 4G SIM proxies, passing all hardware-level security checks.
Q2: How do political CyberTroopers avoid detection by platform algorithms?
They undergo an extended 14-to-30 day account warming process, consuming non-political lifestyle media to accumulate high algorithmic trust scores before handlers inject localized LLM agents generating authentic regional slang.
Q3: How does computational propaganda impact public policy?
By manufacturing the illusion of overwhelming public support or intense backlash, CyberTroopers manipulate politicians into passing controversial legislation, while silencing genuine democratic critics through coordinated intimidation.
Disclaimer: The information presented in this threat intelligence report is for educational and cybersecurity research purposes only. CyberAsia reports on cyber incidents to help organizations understand and defend against emerging threats. We do not provide hacking instructions, host stolen data, or endorse illegal activities.
> INTELLIGENCE_NOTICE
The report above detailing CyberTroopers: 5 Dangerous Ways Politicians Manipulate Voters Online is part of the CyberAsia public archive. For organizations requiring Indicators of Compromise (IoCs), YARA signatures, and specialized malware containment guidelines for threat intelligence threats, please refer to our Secure Drop or contact the research desk.

> ABOUT_AUTHOR: Haider
> related_intel --suggest
Threat Intelligence
 Threat Intelligence
Iran Deploys 2 Cyber Fronts: Handala Targets Israel, CyberAv3ngers Targets US
> read Threat Intelligence