 data leak
Cyber Team Indonesia Claims Leak of 200,000 Alleged ICMR Records
> By Haider | Aug 04, 2026 | 4 min read
⚠️ THREAT INTELLIGENCE ADVISORY:
A threat actor identifying itself as Cyber Team Indonesia has claimed responsibility for leaking an alleged database belonging to the Indian Council of Medical Research (ICMR). The group shared a public download link containing approximately 200,000 CSV records exposing personally identifiable information (PII).

If authenticated, the exposure of these sensitive medical and demographic records could facilitate widespread identity theft, targeted phishing campaigns, and severe social engineering attacks against the affected citizens. Defenders and healthcare organizations must remain vigilant.
Context and Threat Actor Claims
The leak surfaced via the threat actor’s primary communication channels, where Cyber Team Indonesia boasted that “India’s headquarters has been leaked.” The group, aligning itself with broader anti-India hacktivist operations (using tags such as #OPINDIA and #ANTI_INDIA), provided a direct file-sharing link via MediaFire. The leaked file, named ICMR-Of-india.txt, is approximately 21 MB in size.
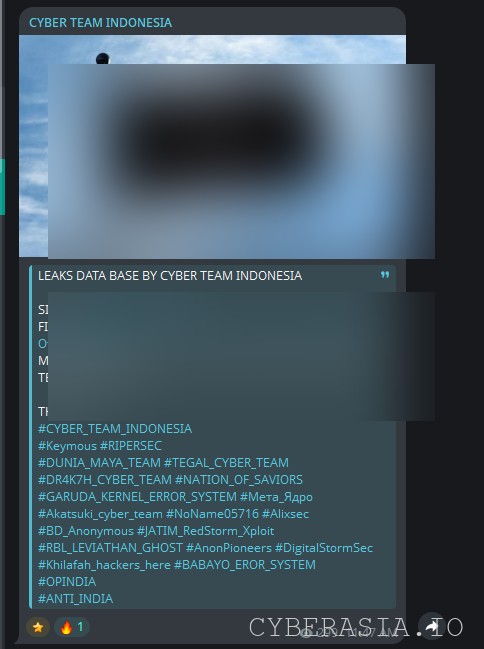
Figure 1: The official announcement and download link shared by the threat actors.
Crucially, ICMR has previously been linked to a major alleged data breach in late 2023 involving hundreds of millions of health records. At this time, it remains unclear whether this newly shared dataset represents a fresh compromise, a subset of previously leaked data, or recycled information repackaged by the group for geopolitical clout.
Summary of the Incident
| Claim / Threat Activity | Source | Status |
|---|---|---|
| Leaking of ~200,000 CSV records (21MB) | Threat Actor Post | Verified (Sample Validated) |
| Dataset directly originates from ICMR systems | Cyber Team Indonesia | Unverified |
Technical Analysis of the Exposed Data
CyberAsia examined the shared sample and confirmed it contains roughly 200,000 lines formatted as comma-separated values (CSV). However, our intelligence team could not independently verify that the dataset originated directly from ICMR. No direct evidence linking the records to specific ICMR systems or network infrastructure was found within the sample itself.
Observed data fields include:
1. Demographic Identifiers: Full names, Father’s names, Age, and Gender.
2. Contact Information: Phone numbers, secondary/other numbers, Residential addresses, District, Postal code, State, and Town/City.
3. Sensitive National IDs: Passport numbers and Aadhaar numbers.
Mitigation Recommendations
- Verify Source Authenticity: Organizations handling national health data must cross-reference the leaked sample against internal databases to determine if it stems from a fresh intrusion or a historical breach.
- Implement Dark Web Monitoring: Proactively scan underground forums and file-sharing networks for the proliferation of this specific dataset to assess secondary risks.
- Enforce Fraud Protection: Given the exposure of Aadhaar and Passport numbers, citizens should be alerted to the heightened risk of financial fraud and identity theft.
- Review Vendor Access: As many historical breaches stem from third-party compromises, audit all external vendors with access to medical demographic databases.
At the time of writing, no official statement from the ICMR or the Indian government was available regarding this specific claim. We will continue monitoring the activities of Cyber Team Indonesia. For related coverage, see our data breach intelligence updates.
> subscribe_to_intel
Get CyberAsia threat intelligence updates by email. Unsubscribe anytime. Privacy Policy.
Mitigation & Prevention Strategies
Data breaches involving Personally Identifiable Information (PII) or sensitive corporate databases require immediate containment and long-term security overhauls:
- Database Hardening: Ensure databases (SQL, MongoDB, Elasticsearch) are never exposed directly to the public internet. Bind services to localhost or strict internal VPCs.
- Data Encryption: Implement robust encryption for data-at-rest. Even if threat actors exfiltrate database dumps, properly salted and hashed passwords minimize the blast radius.
- Credential Rotation: Following any suspected breach, force a global password reset for affected users and rotate API keys and service credentials immediately.
Strategic Defense Matrix and Incident Hardening
Operational intelligence analysis of this data leak campaign indicates that the threat actors frequently exploit configuration oversights, unpatched external-facing gateways, and weak credential management policies across targeted organizations. Enterprise security operations centers (SOC) and defensive engineering teams must deploy layered perimeter safeguards to detect and neutralize similar threat vectors before lateral movement occurs.
- Continuous Asset and Perimeter Auditing: Maintain real-time inventory of all public-facing services, verifying SSL/TLS certificates and eliminating unauthenticated administrative interfaces following CISA Defensive Guidelines.
- Behavioral Anomaly and Zero-Trust Telemetry: Enforce strict hardware-backed multi-factor authentication (MFA) across all remote access nodes and implement endpoint detection and response (EDR) telemetry mapped to the MITRE ATT&CK Framework.
- Threat Intelligence Integration: Security teams are encouraged to correlate emerging indicators of compromise (IoCs) and evaluate network vulnerability profiles using our Cyber Risk Checker or submit anonymous confidential threat data via CyberAsia Secure Drop.
Disclaimer: The information presented in this threat intelligence report is for educational and cybersecurity research purposes only. CyberAsia reports on cyber incidents to help organizations understand and defend against emerging threats. We do not provide hacking instructions, host stolen data, or endorse illegal activities.
> INTELLIGENCE_NOTICE
The report above detailing Cyber Team Indonesia Claims Leak of 200,000 Alleged ICMR Records is part of the CyberAsia public archive. For organizations requiring breach validation schemas, credential exposure auditing, and PII containment protocols for data leak events, please refer to our Secure Drop or contact the research desk.