 ddos
ddos
Yemen Cyber Group Attacks Israeli Sites: 4 Critical Domains Suffer Outages
> By Clara | Sep 05, 2026 | 4 min read
A coordinated distributed denial of service offensive under the Yemen Cyber Group Attacks Israeli Sites campaign has disrupted access to prominent legal, consumer technology, and non-profit gateways across Israel, overwhelming origin web servers with persistent Layer 7 connection stress.

The operational release, syndicated across underground Telegram channels associated with the Yemen Cyber Group and tagged under the long-running #OpIsrael banner, targeted four distinct targets in rotation: international intellectual property law firm Pearl Cohen (pearlcohen.com), corporate responsibility forum Maala (maala.org.il), non-profit organization Mada (mada.org.il), and navigation device vendor Garmin Israel (garmin.co.il).
Yemen Cyber Group Attacks Israeli Sites: 4 Disrupted Sectors Analyzed
Technical diagnostic captures gathered during the strike reveal distinct infrastructure failure modes across each targeted property. For international patent and technology litigation firm Pearl Cohen, public gateways returned an explicit Cloudflare Error 522 Connection Timed Out notification. In high-traffic network architectures, Error 522 demonstrates that while Cloudflare Anycast edge servers successfully established TCP handshakes with client browsers, the origin hosting infrastructure failed to respond within the default 15-second timeout window.
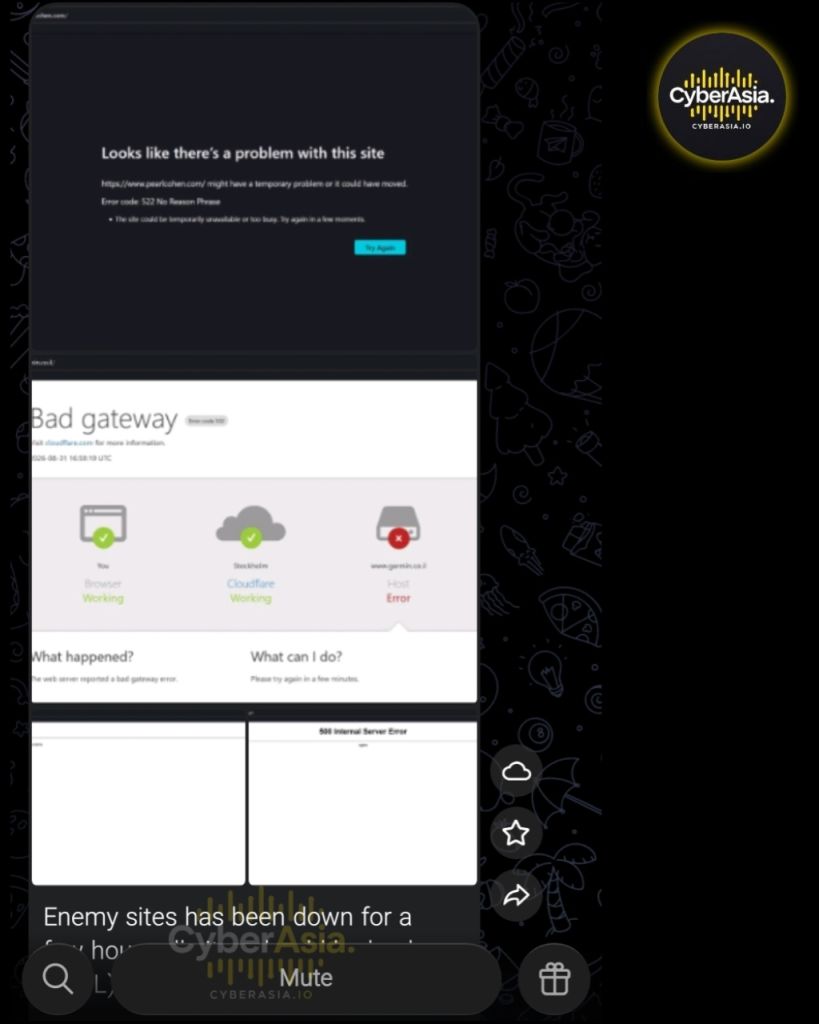
Concurrently, the consumer technology portal for Garmin Israel exhibited an Error 502 Bad Gateway failure. Diagnostic telemetry recorded via third-party monitoring nodes confirmed that edge proxy clusters in Stockholm remained functional, but upstream application servers failed to return valid HTTP response headers, indicating localized web server socket exhaustion under sustained concurrent requests.
Network Telemetry and Third-Party Check-Host Diagnostics
Multi-region verification links published by the threat actors via check-host.net documented systematic availability drops across international test locations. Handshake latency across European, North American, and Asian sensors registered repeated connection refusal and timeout states during peak strike windows.
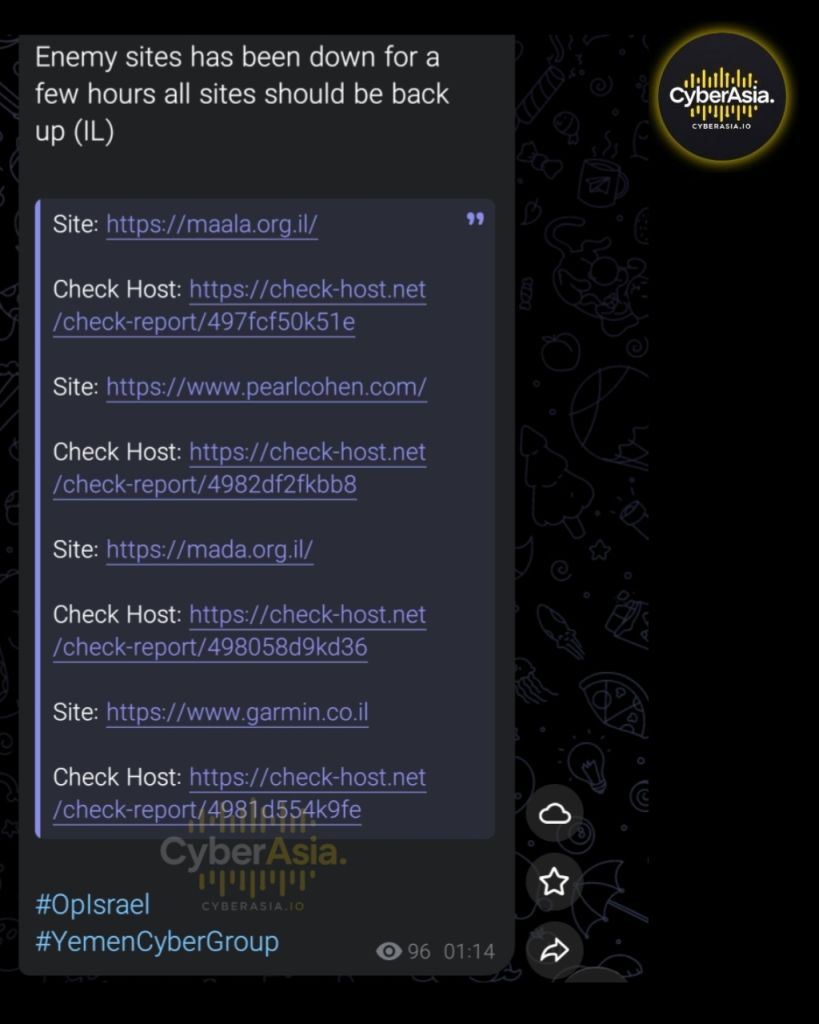
In their Telegram bulletin, the actors openly acknowledged the transient nature of the assault, stating: “Enemy sites has been down for a few hours all sites should be back up (IL).” This communication pattern matches known tactical playbooks within hacktivist stresser syndicates, where transient server disruption is maximized for social media propaganda value rather than sustained long-term denial.
Forensic assessment confirms zero unauthorized access to underlying corporate databases, customer credentials, or sensitive intellectual property files. The entire operational footprint was restricted to application-layer HTTP flood stress testing against outward-facing marketing and reference portals.
Threat Actor Profile: Yemen Cyber Group Operational Cadence
The Yemen Cyber Group operates as a politically motivated hacktivist cell focusing on symbolic targets linked to the Middle Eastern geopolitical theater. While their rhetoric frequently mirrors regional militant narratives, their observed offensive capabilities center primarily around commercial stresser tooling, public botnets, and opportunistic website defacements rather than bespoke zero-day exploits or state-level advanced persistent threat (APT) toolchains.
By selecting diverse sectors spanning legal advisory services, national non-profits, and consumer electronics retail, the group leverages target diversity to project broad offensive reach across digital media channels.
Frequently Asked Questions
Q1: Was client legal data or Garmin customer telemetry stolen in this attack?
No. Technical telemetry confirms that backend databases, customer account portals, and internal document management systems remained unaffected. The incident was exclusively an HTTP Layer 7 availability disruption against public landing portals.
Q2: Why did Cloudflare Error 522 and 502 appear if CDN protection was active?
While Cloudflare edge nodes absorb volumetric bandwidth floods, Layer 7 HTTP request spikes bypass basic DNS shields by generating legitimate-looking application requests. When the origin web server exhausts its worker processes, Cloudflare returns Error 522 (Origin Timeout) or Error 502 (Bad Gateway).
Q3: What immediate defensive configurations mitigate Layer 7 origin timeout floods?
Enterprise administrators must enforce active Cloudflare Under Attack Mode (UAM) or Turnstile challenge rules, implement per-IP rate-limiting on origin web servers (Nginx/Apache), verify origin IP shielding to block direct-to-origin bypasses, and configure static edge caching for landing pages.
This report is compiled strictly for cyber threat intelligence, defensive engineering, and educational research purposes based on verified open-source data and network telemetry. CyberAsia urges enterprise defenders to implement recommended edge mitigation protocols and never engage in unlawful network stress activities.
Disclaimer: The information presented in this threat intelligence report is for educational and cybersecurity research purposes only. CyberAsia reports on cyber incidents to help organizations understand and defend against emerging threats. We do not provide hacking instructions, host stolen data, or endorse illegal activities.
> INTELLIGENCE_NOTICE
The report above detailing Yemen Cyber Group Attacks Israeli Sites: 4 Critical Domains Suffer Outages is part of the CyberAsia public archive. For organizations requiring real-time attack telemetry, check-host latency records, and edge firewall mitigation strategies for ddos incidents, please refer to our Secure Drop or contact the research desk.