Defacement
~/ › Defacement › article
Defacement
onehuman.family Targeted in Cyberattack: 1 Critical Web Defacement Exposed
> By datojohnny | Aug 27, 2026 | 3 min read
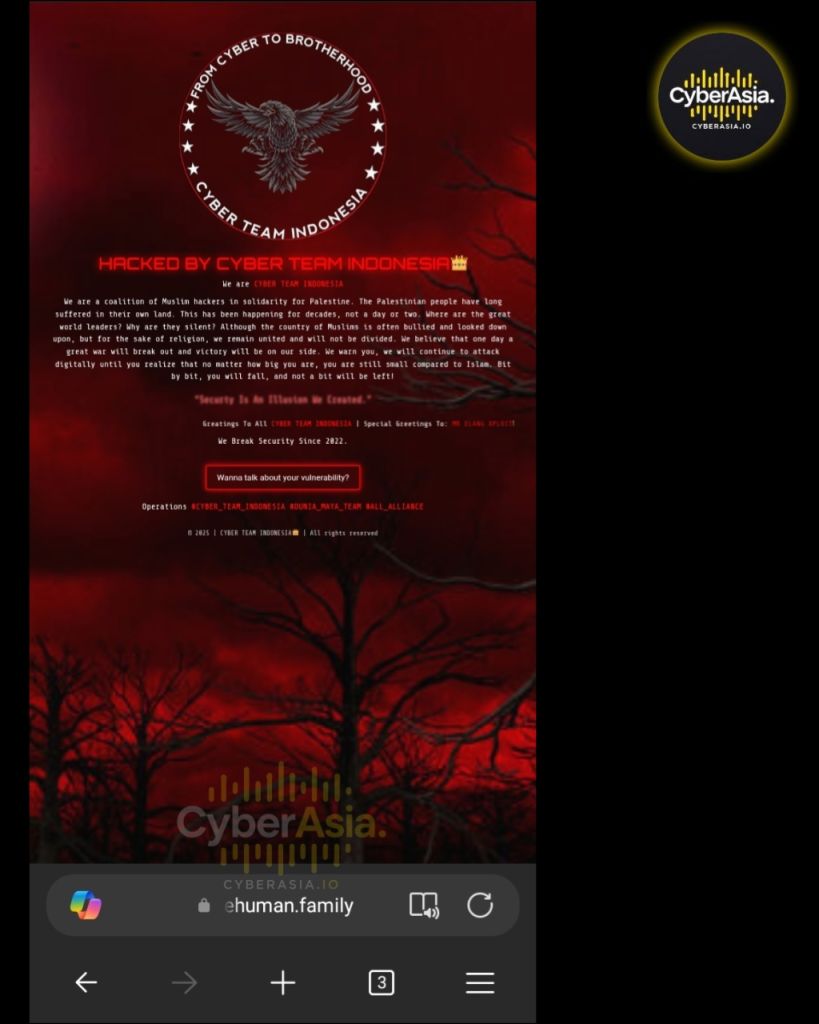
An ideological web tampering campaign has disrupted international civic digital assets as onehuman.family targeted in cyberattack operations saw Indonesian hacktivists replace the site’s primary landing portal with a customized political defacement script.
Visitors navigating to onehuman.family were greeted by a dark red interface featuring silhouettes of barren trees beneath an eagle crest emblazoned with the declaration “Hacked By Cyber Team Indonesia.” The operation represents a classic web defacement, an integrity attack executed to project political messaging and capability rather than immediate data exfiltration.
Technical Forensics: How onehuman.family Targeted in Cyberattack Occurred
Forensic inspection of the defaced DOM structure indicates that the attackers successfully altered the index rendering file within the website’s Content Management System (CMS). Common intrusion vectors for this operational profile include exploitation of unpatched CMS plugin vulnerabilities, credential stuffing against administrative panels, or insecure file upload bypasses.
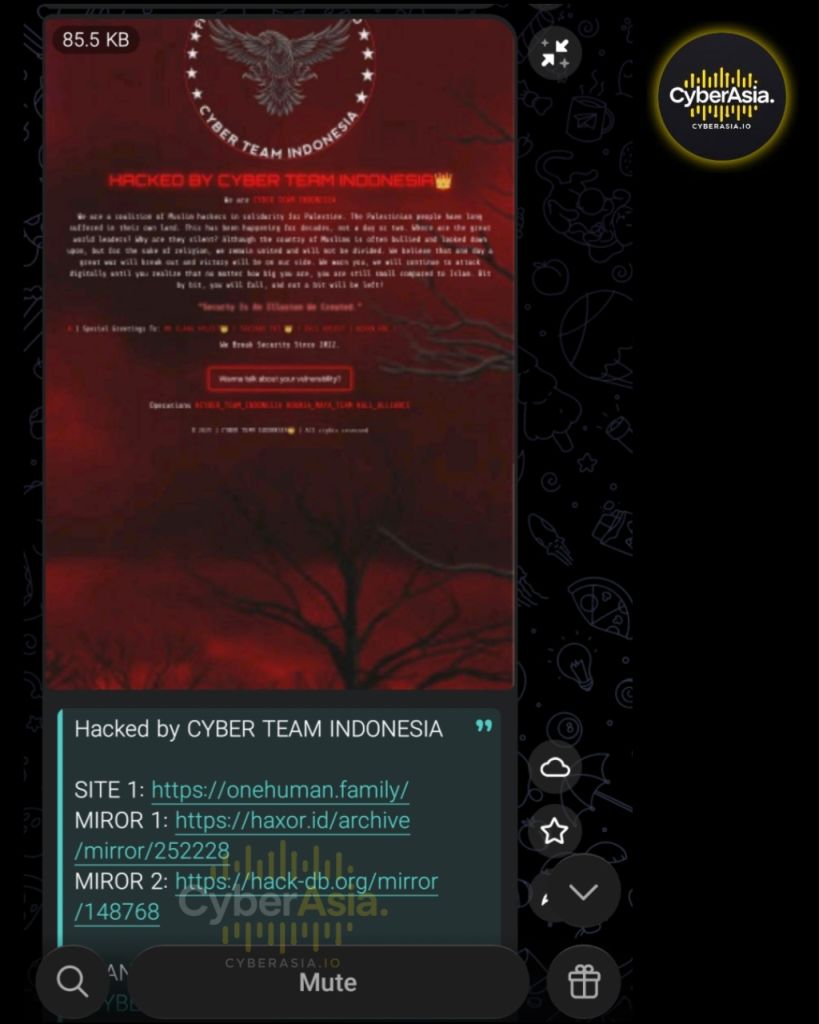
The injected payload prominently featured the slogan “Security Is An Illusion We Created,” accompanied by a manifesto expressing solidarity with Palestine. The actors included an interactive button titled “Wanna talk about your vulnerability?” linked to an external Telegram communications handle, a psychological provocation technique frequently employed by regional hacktivist collectives.
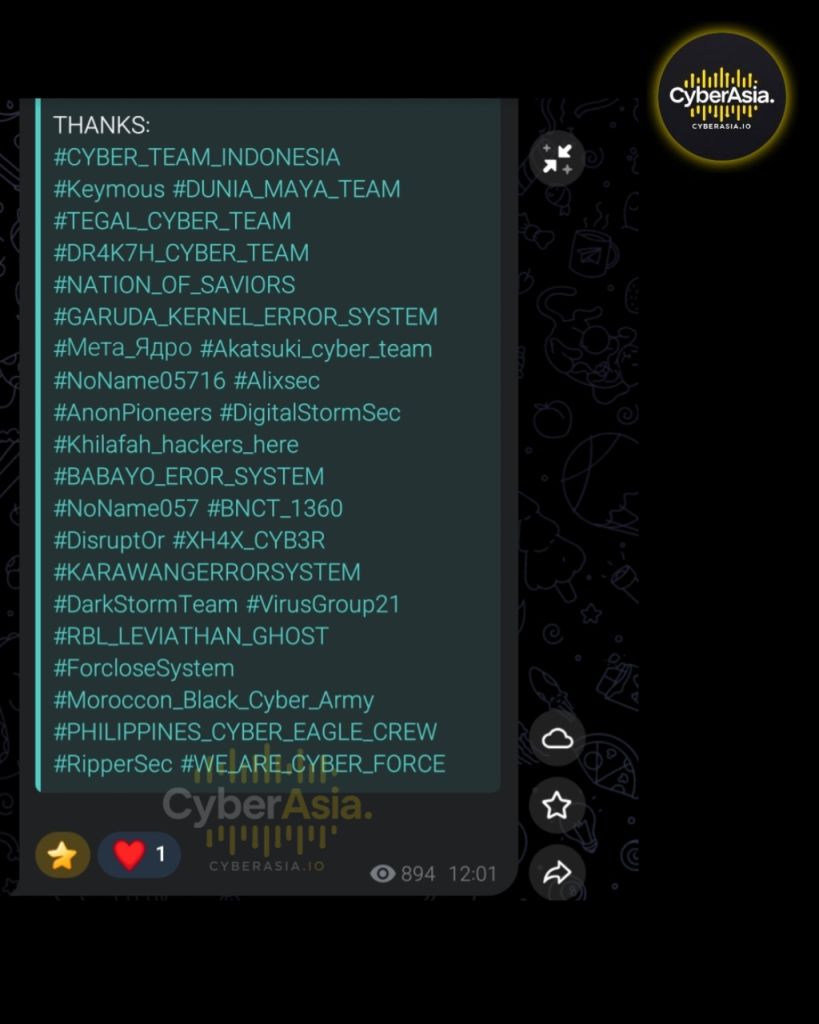
The defacement signature credited multiple affiliated collectives across the Southeast Asian and international underground, including Dunia Maya Team, Keymous, Philippines Cyber Eagle Crew, and the Moroccan Black Cyber Army.
Threat Actor Profile: Cyber Team Indonesia
Cyber Team Indonesia has maintained an active presence in regional defacement archives since 2022. Their primary modus operandi focuses on automated vulnerability scanning of exposed WordPress and custom web applications, weaponizing identified misconfigurations to publish public mirror archives on platforms like Zone-X and Defacer.id.
Technical verification confirms that while the web root directory was overwritten to host the defacement layout, backend MySQL databases remained intact, with no evidence of persistent webshell backdoors or exfiltration of sensitive organizational records.
Frequently Asked Questions
Q1: Was donor or user information stolen during the onehuman.family defacement?
No. Technical investigation confirms that the attack was confined to presentation-layer file overwriting. No database dumps, credit card details, or PII were exfiltrated during the incident.
Q2: How do threat actors gain administrative access to deface website homepages?
Attackers typically exploit vulnerable third-party plugins, outdated CMS software components, weak administrative FTP/SSH passwords, or misconfigured file permissions that permit arbitrary file uploads.
Q3: What immediate remediation steps are required following a web defacement?
Administrators must immediately revoke all existing session tokens, reset administrative passwords across CMS and hosting panels, restore clean files from offline backups, deploy a Web Application Firewall (WAF), and enforce strict file integrity monitoring (FIM).
This report is compiled strictly for cyber threat intelligence, defensive engineering, and educational research purposes based on verified open-source data and network telemetry. CyberAsia urges website operators to implement recommended defensive hardening and never engage in unlawful cyber operations.
Disclaimer: The information presented in this threat intelligence report is for educational and cybersecurity research purposes only. CyberAsia reports on cyber incidents to help organizations understand and defend against emerging threats. We do not provide hacking instructions, host stolen data, or endorse illegal activities.
> INTELLIGENCE_NOTICE
The report above detailing onehuman.family Targeted in Cyberattack: 1 Critical Web Defacement Exposed is part of the CyberAsia public archive. For organizations requiring real-time attack telemetry, check-host latency records, and edge firewall mitigation strategies for defacement incidents, please refer to our Secure Drop or contact the research desk.