Defacement
~/ › Defacement › article
Defacement
Legacy Event Hall’s Florida Site Hacked, Replaced With Anti-Israel Message
> By Clara | Aug 21, 2026 | 7 min read
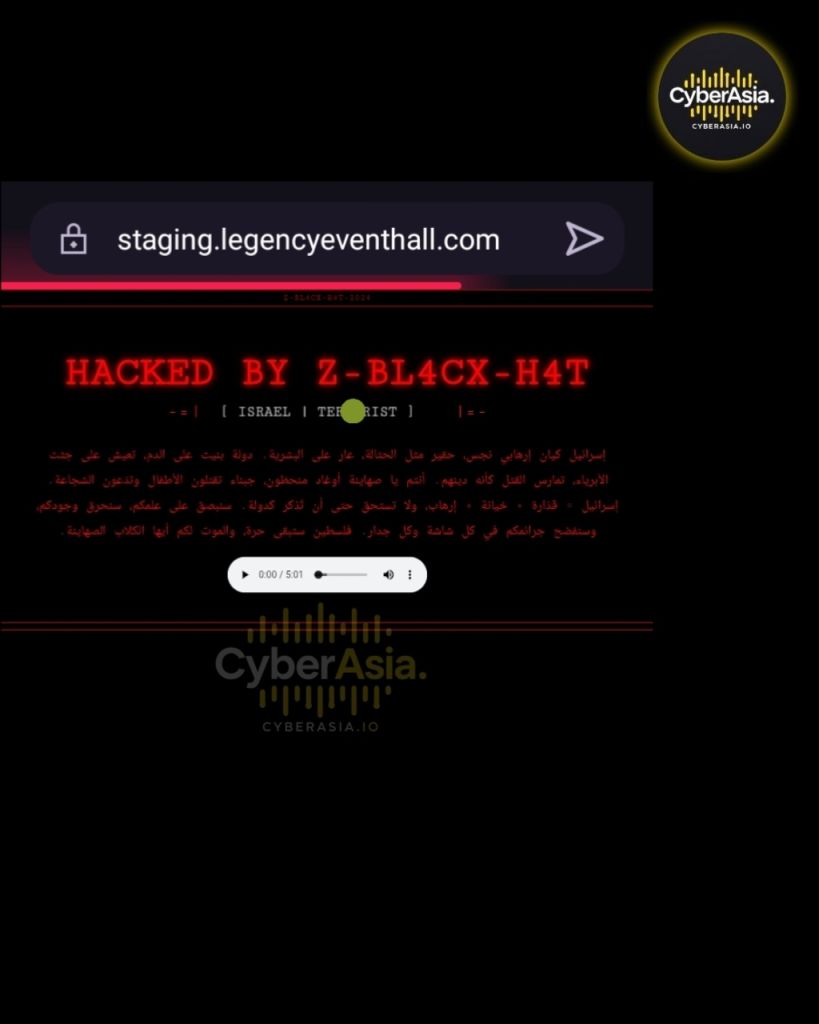
A staging subdomain belonging to an event venue provider based in Orlando, Florida, United States, was hacked and underwent a drastic visual change after CyberAsia’s monitoring team detected a post displaying evidence of the breach. The page, which previously showed service information for event hall rentals, now displays a red-and-black banner reading “Hacked by Z-BL4CX-H4T,” accompanied by Arabic script at the top and a lengthy political message in Arabic directed against Israel.
The incident first surfaced on a threat intelligence monitoring channel that CyberAsia’s team regularly uses to track the activity of ideologically motivated hacking groups. The post included a screenshot of the hacked page, the target address, and the identity used by the actor to sign off on the action.
What Happened
According to the screenshots circulating, the hacked page is located at staging.legencyeventhall.com , a staging subdomain commonly used by web developers to test a site’s appearance or features before it is officially published to the main domain. Staging environments like this are often subject to less rigorous security oversight than production sites, making them a frequent entry point for opportunistic attackers.
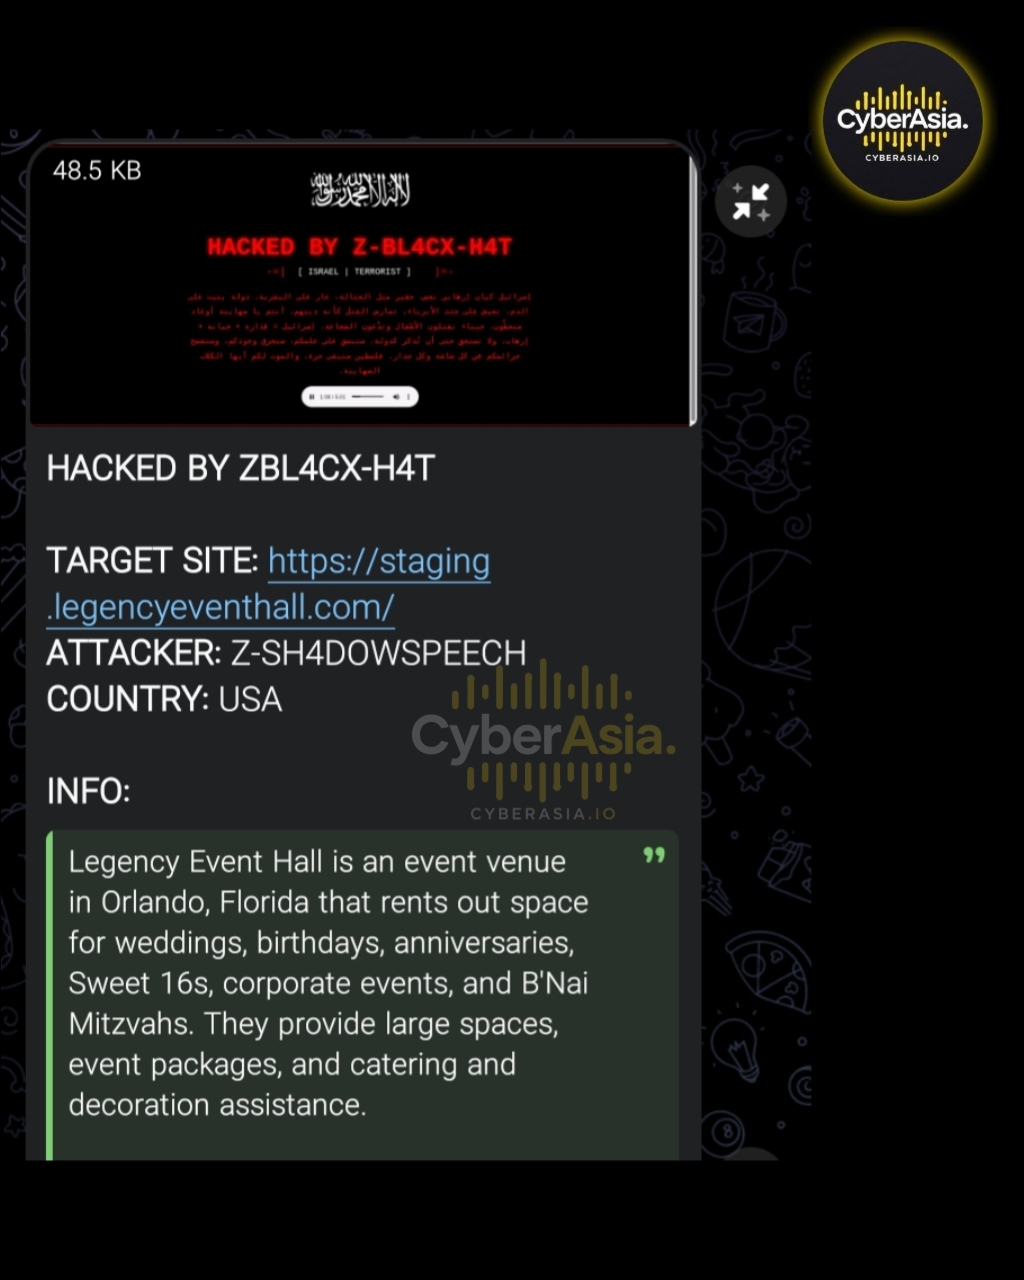
The hacked page shows large red text reading “HACKED BY Z-BL4CX-H4T” at the top, followed by the label “[ISRAEL | TERR*RIST]” and a long block of Arabic text. The text is a political statement accusing Israel of atrocities against Palestinian civilians, delivered with harsh rhetoric toward the country. CyberAsia has chosen not to reproduce the statement verbatim, as it contains inflammatory language that offers no additional informational value to readers beyond confirming the actor’s ideological motive.
Below the main banner, the hacked page also embeds an audio player roughly five minutes in length, though the exact content of the audio cannot be confirmed from the circulating screenshots.
Notably, the same post also lists a set of operation hashtags indicating a broader campaign beyond this single target, covering the United Kingdom (#OpUnitedKingdom), the United States (#OpUnitedStates), Israel (#OpIsrael), France (#OpFrance), and Italy (#OpItaly). This naming pattern is common among hacktivist groups that rotate through multiple Western countries as part of a symbolic campaign, rather than executing a technically sophisticated attack on critical infrastructure.
Who Is Affected
The target in this incident is Legacy Event Hall, an event venue provider based in Orlando, Florida. Based on the description accompanying the hack post, the business rents out space for a range of events, including weddings, birthdays, and anniversaries. It also serves Sweet 16 celebrations, corporate events, and B’Nai Mitzvah celebrations , a Jewish religious tradition marking a child’s entry into religious responsibility.
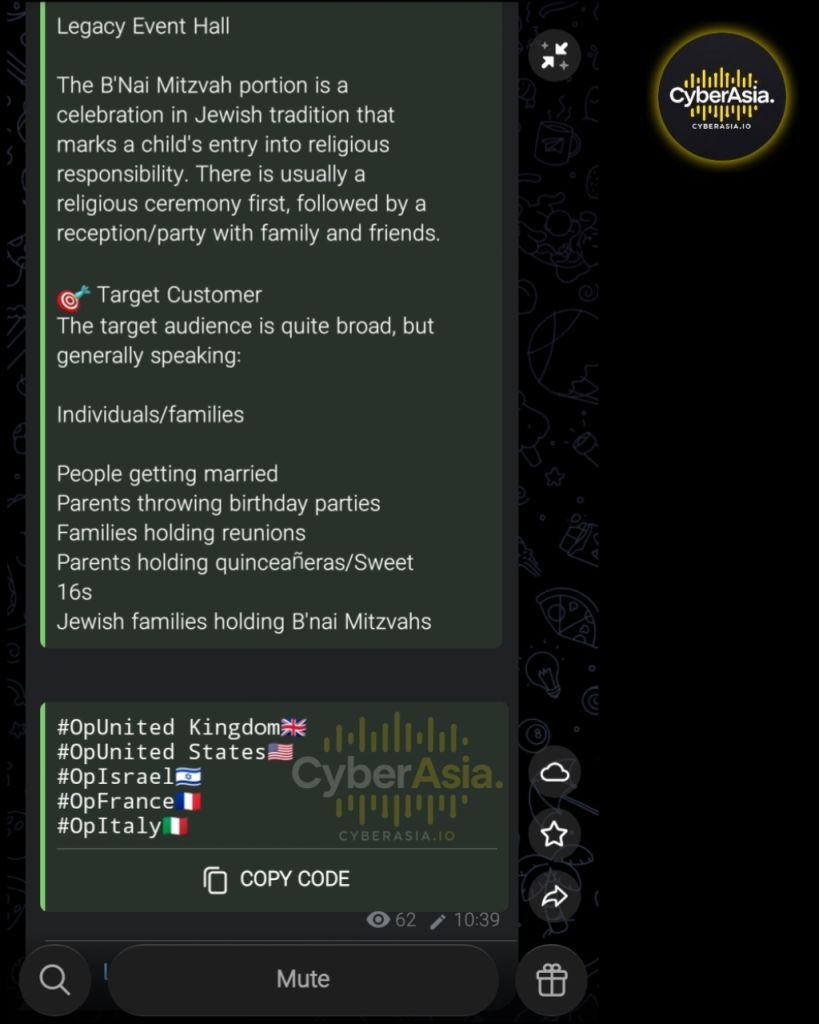
Given the venue’s client base, which includes the Jewish community celebrating B’Nai Mitzvahs, the choice of target appears unlikely to be random. The actor seems to have specifically singled out a business with a symbolic connection to the Jewish community, aligning with the anti-Israel narrative inserted into the hacked page.
So far, there is no indication from the circulating screenshots that customer data, event booking information, or payment details were affected. The visible impact of the incident so far is limited to a change in the staging page’s appearance, not evidence of data exfiltration.
Technical Details
On the technical side, available information remains limited to what is displayed directly on the hacked page. The altered file was recorded at 48.5 KB, a relatively small size consistent with a simple static defacement page containing only text, symbolic imagery, and an embedded media player, without complex backend functionality.
The target is a staging subdomain, not the main production domain. This is worth noting, as staging environments typically:
- Use looser access credentials compared to production environments.
- Often still run on default configurations or built-in passwords from development tools (CMS, hosting panels, or web frameworks).
- Frequently lack the same security monitoring systems (WAF, IDS/IPS) applied to the main domain.
- Sometimes remain publicly accessible even though they are intended only for internal team use.
The exact method the actor used to hack into the subdomain is not explained in the circulating material. There is no mention of a specific CVE, plugin vulnerability, or particular software flaw in the post. This means the initial intrusion technique , whether through leaked credentials, a CMS vulnerability, a server misconfiguration, or another method , remains an area that would need further investigation by the relevant authorities or Legacy Event Hall’s own security team.
Threat Actor and Background
The name signed onto this hack is “Z-BL4CX-H4T,” while the individual identity listed in the post operates under the alias “Z-SH4DOWSPEECH” and lists the United States as its country of origin. This combination of a group identity and an individual alias is common within underground hacking communities, where a single group “brand” is shared by several individuals who each take credit for their own actions under it.
The style of the message , religious symbolism at the top of the page, the “TERR*RIST” label directed at Israel, a lengthy Arabic-language political statement, and a list of cross-country operation hashtags , is highly consistent with the pattern of pro-Palestinian hacktivist groups that have, over the past several years, hacked and defaced small and medium-sized websites in Western countries as a form of symbolic protest against Israeli policy and its allies.
Groups following this pattern typically do not select targets based on a direct connection to the geopolitical conflict itself. Instead, they favor targets that are technically easy to hack (low-hanging fruit), then leverage the target’s name or symbolic affiliation , in this case, its B’Nai Mitzvah services , to reinforce their campaign narrative across social media and Telegram channels.
Potential Impact
Although this incident amounts to a straightforward website hack with no indication of data theft, its impact still warrants serious attention from the business owner, particularly on the reputational front. For a small-to-medium-sized business like an event venue provider, prospective clients’ trust in the security of their booking and personal information is an important factor in their decision to transact.
Other potential impacts worth watching include:
- Short-term reputational risk if screenshots of the hacked page spread widely on social media before the site is restored.
- The possibility that the same staging environment stores credentials or configurations that could be leveraged to pivot toward the main production domain, if the two environments share infrastructure or credentials.
- Psychological effects on staff and management upon discovering their business was hacked due to a symbolic association with a particular community, despite having no political intent themselves.
- The potential for repeat targeting, given that hacktivist groups of this kind tend to hack more than one target within the same campaign wave, as reflected in the multi-country list of operation hashtags included in the post.
Response and Mitigation
As of this writing, there has been no official statement from Legacy Event Hall regarding the incident. CyberAsia continues to monitor whether the staging subdomain has been restored to its normal state or still displays the hacked page.
For business owners and website administrators in general, this incident serves as a reminder of several basic mitigation steps that are often overlooked, particularly for staging environments:
- Restrict access to staging subdomains to internal networks only, or require additional authentication such as VPN access and IP whitelisting.
- Use unique, strong passwords for each environment, and avoid reusing staging credentials in production.
- Regularly update the CMS, plugins, and frameworks in use, including in staging environments.
- Conduct periodic audits of active but rarely monitored subdomains, as “forgotten” subdomains are a favorite entry point for attackers.
- Establish an incident response procedure that includes rapid recovery steps and transparent communication with customers should a similar incident occur on the production domain.
Conclusion
This incident involving Legacy Event Hall’s hacked staging subdomain illustrates a typical pattern of ideologically motivated hacktivist attacks: targets are chosen not for the value of the data they hold, but for their symbolic association with the geopolitical cause the actor is championing. Although the technical impact is limited to a change in the page’s appearance, the incident is a reminder that small and medium-sized businesses, including event venue providers, are not immune from being swept into cross-border cyber campaigns.
With a list of operations spanning at least five different countries, the group claiming responsibility for this hack is likely to continue seeking new targets following a similar pattern in the near future. CyberAsia will continue monitoring this group’s activity, along with the possibility of additional targets emerging in the same region.
Disclaimer: CyberAsia is an independent Cyber Threat Intelligence (CTI) research organization. The information provided in this report is derived from public intelligence gathering, dark web monitoring, and threat actor claims. It is published strictly for educational purposes, defensive analysis, and public awareness. CyberAsia does not endorse, verify, or facilitate any cyberattacks or illegal activities.
> INTELLIGENCE_NOTICE
The report above detailing Legacy Event Hall’s Florida Site Hacked, Replaced With Anti-Israel Message is part of the CyberAsia public archive. For organizations requiring real-time attack telemetry, check-host latency records, and edge firewall mitigation strategies for defacement incidents, please refer to our Secure Drop or contact the research desk.