 data leak
France Utilitaires Data Breach: LunarisSec Exposes 8 Records
> By Clara | Oct 15, 2026 | 6 min read
The France Utilitaires data breach came into public view on October 13, 2026, when Algeria-linked group LunarisSec posted screenshots of a customer table tied to france-utilitaires.fr. The group published the material on its official messaging channel and on X, and wrote that the French website “had a critical vulnerability.”
The images show eight visible rows with blurred customer names, pre-tax totals and request dates. The newest entries are stamped October 12, 2026, only a day before the announcement. No statement from the company appears in the material reviewed for this report.
France Utilitaires Data Breach: What LunarisSec Published
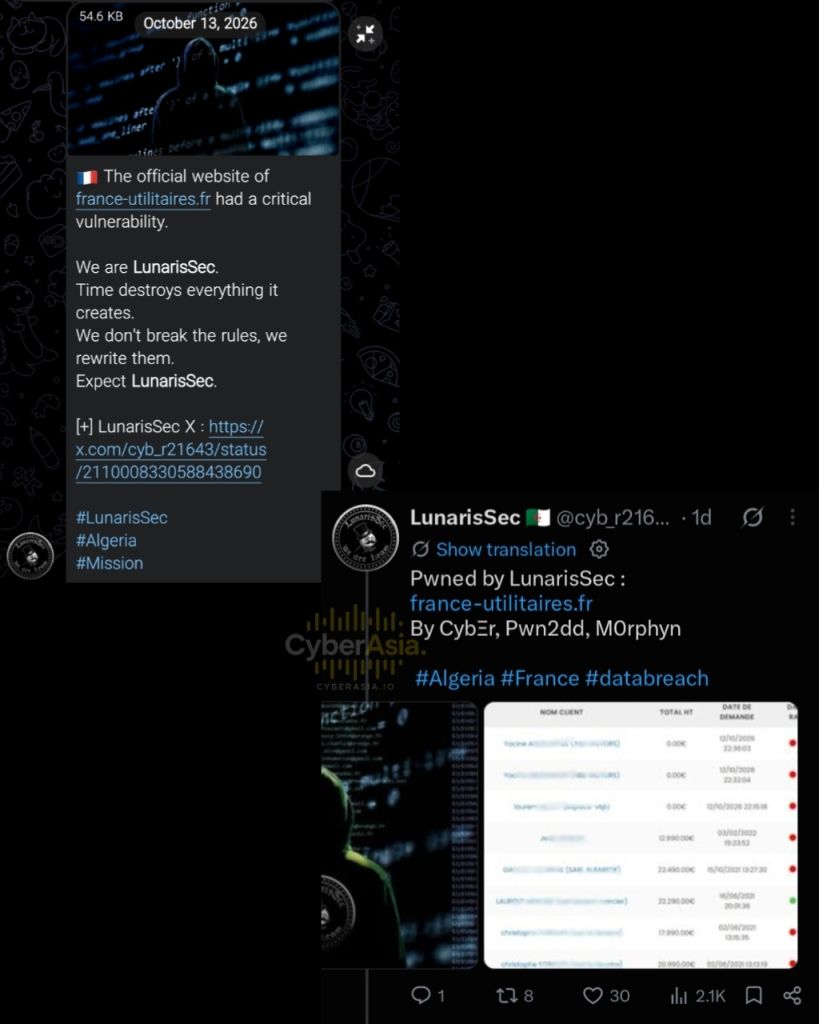
The first post is a short message dated October 13, 2026. It opens with a French flag and the line about the vulnerability, then switches to the group’s slogan: “Time destroys everything it creates. We don’t break the rules, we rewrite them. Expect LunarisSec.” It links to an X post from the handle @cyb_r21643 and closes with the hashtags #LunarisSec, #Algeria and #Mission.
The X post is more specific. It reads “Pwned by LunarisSec,” names the domain, and credits three members: CybΞr, Pwn2dd and M0rphyn. The hashtags are #Algeria, #France and #databreach. At the time of capture it showed one reply, eight reposts, 30 likes and 2.1K views.
Neither post names a vulnerability type, a record count or a download link. Neither contains a ransom demand or payment instruction.
Inside the France Utilitaires Data Breach Screenshot
The second attachment on the X post is a white table in French. The readable headers are NOM CLIENT (customer name), TOTAL HT (total before tax) and DATE DE DEMANDE (request date). A fourth column is cut off at the right edge. Customer names are blurred, and only fragments remain.
Eight rows are visible and they run from newest to oldest. The three most recent entries are dated October 12, 2026, at 22:36:03, 22:32:04 and 22:15:18, and each shows a total of 0.00 euros. That could point to requests not yet priced, although the screenshot does not explain it.
The other five rows carry totals of 12,990, 22,490, 22,290, 17,990 and 20,990 euros, with request dates between June 2, 2021 and February 3, 2022. Together those five come to 96,750 euros before tax.
The domain name refers to light commercial vehicles, and totals in that range would fit vehicle quotes. The screenshot itself does not say what the business sells. At least one row carries a company label in brackets, which suggests business customers sit alongside individuals. Most rows show a red status dot at the right edge and one shows green. The meaning of the colors is not explained.
The layout looks like a back-office list sorted by request date, which is an inference and not something the group stated.
The dark image of a hooded figure over lines of code also contains faint text that resembles email addresses, but it is too small to read reliably.
Who Is LunarisSec?
LunarisSec uses a round emblem showing a cartoon gentleman in a top hat, with a monocle and a mustache, surrounded by stars and the words “we are team.” Its X account displays an Algerian flag, and the hashtags in its posts point to Algeria as its stated base.
The France Utilitaires data breach is not the group’s first French target this month. On October 10, 2026, three days earlier, it posted about infogreffe.fr under the same hashtags, #Algeria, #France and #databreach. CyberAsia covered that post in https://cyberasia.io/article/data-leak/lunarissec-infogreffe-alert/: LunarisSec infogreffe.fr data breach coverage]. Two French targets in one week suggest France is the current focus.
What the Evidence Does Not Show
Screenshots can show that a table exists. They cannot show how it was obtained, how large the full dataset is, or whether it matches live records. The group has not said which flaw it used, and nothing in the posts shows contact with the company before publication.
Because the names are blurred, CyberAsia cannot say which individuals are affected. What can be said is narrower: a hacktivist group put its name on a France Utilitaires data breach and published a structured customer listing as supporting material.
Risks After the France Utilitaires Data Breach
If the records are genuine, the immediate risk is impersonation rather than account takeover. A criminal holding a name, a quote amount and a request date can write a convincing message that appears to come from a dealer or finance partner. Typical lures include a payment confirmation, a request to resend identity documents, or new bank details for a deposit.
Business customers face invoice fraud, which works best when the sender knows the amount and timing of a real purchase. Treat any message that changes payment details as suspicious until it is confirmed by phone.
Response Steps for the Company and Customers
For the company, the first tasks are standard. Close the vulnerable component, rotate administrator and database credentials, preserve logs, and review access around October 12 and 13, 2026. Under the GDPR, a confirmed personal data breach generally has to be reported to the CNIL within 72 hours of the company becoming aware of it, and to individuals when the risk to them is high.
For customers, avoid clicking links in unexpected messages about a quote, and do not send documents or payments on request without calling to check. Change any reused passwords. Suspicious messages can be reported through Cybermalveillance.gouv.fr, the French government platform that assists victims of cybercrime.
FAQ
Q1 : Is customer data from france-utilitaires.fr really leaked?
The screenshots show a customer table with totals and request dates, and the group says the site had a critical vulnerability. No download link, record count or technical detail is given, and the company has not responded in the material reviewed. The real scope of the France Utilitaires data breach is therefore unknown.
Q2 : What kind of vulnerability was used?
The posts do not say. Incidents like this often involve injection flaws or broken access control, but nothing in the screenshots confirms either one.
Q3 : What should customers who requested a quote do now?
Treat unexpected calls, emails and texts that mention a quote, a deposit or a payment as suspicious, and verify any change in bank details by phone with the company.
Research Note: This article is published for educational cyber security research and awareness purposes only. CyberAsia.io does not condone unauthorized access to computer systems and does not host or distribute stolen data. Details reflect the material reviewed at the time of writing and may change as new information becomes available.
Disclaimer: The information presented in this threat intelligence report is for educational and cybersecurity research purposes only. CyberAsia reports on cyber incidents to help organizations understand and defend against emerging threats. We do not provide hacking instructions, host stolen data, or endorse illegal activities.
> INTELLIGENCE_NOTICE
The report above detailing France Utilitaires Data Breach: LunarisSec Exposes 8 Records is part of the CyberAsia public archive. For organizations requiring breach validation schemas, credential exposure auditing, and PII containment protocols for data leak events, please refer to our Secure Drop or contact the research desk.