 ddos
ddos
TheGarudaEye DDoS Hits Saudi eVisa, SWA: 2 Critical Outages
> By Clara | Oct 17, 2026 | 6 min read
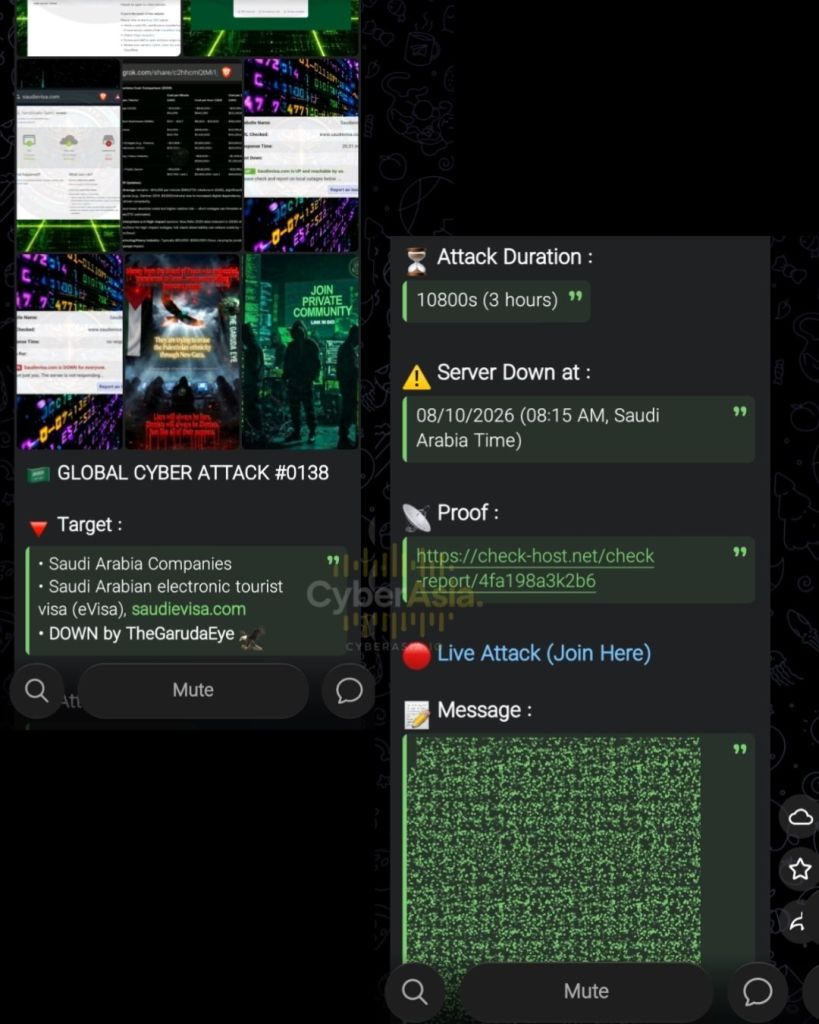
TheGarudaEye DDoS attacks took two Saudi websites offline in under 24 hours, based on the group’s own announcements and the outage screenshots posted with them. The visa portal saudievisa.com went down at 08:15 AM Saudi time on 8 October 2026. The public website of the Saudi Water Authority, swa.gov.sa, followed at 08:00 AM on 9 October 2026.
The group numbered the incidents Global Cyber Attack #0138 and #0139, and stated a duration of 10,800 seconds, or three hours, for each. Supporting material included check-host reports, Cloudflare error pages, and uptime checker captures. The material reviewed for this report contains no response from either organization.
> TABLE_OF_CONTENTS [toggle]
- > TheGarudaEye DDoS Timeline: Two Outages, One Campaign
- > Attack #0138: Saudi eVisa Portal Goes Dark
- > Attack #0139: Saudi Water Authority Returns Error 522 and 503
- > What the Error Codes Suggest About the Attack Method
- > OpSaudiArabia and OpBoP: The Message Behind the Outages
- > How Admins Can Reduce DDoS Downtime
- > FAQ
- > Research Notice
TheGarudaEye DDoS Timeline: Two Outages, One Campaign
Both posts follow one template: a target list, a duration, a server down time, a proof link, a message block, and a thanks line. The sequential numbering points to a running series, although earlier entries were not part of the material reviewed.
| Item | Attack #0138 | Attack #0139 |
| Target | saudievisa.com | swa.gov.sa |
| Listed category | Saudi Arabia Companies | Saudi Arabia Government |
| Stated start (Saudi time) | 8 Oct 2026, 08:15 AM | 9 Oct 2026, 08:00 AM |
| Stated duration | 10,800 seconds | 10,800 seconds |
| Error evidence | SSL handshake failure | Error 522 and HTTP 503 |
The two start times sit 23 hours and 45 minutes apart.
Attack #0138: Saudi eVisa Portal Goes Dark
The first announcement lists Saudi Arabia Companies and the Saudi Arabian electronic tourist visa as targets, with saudievisa.com named explicitly. It records the outage start as 08:15 AM Saudi time on 8 October 2026 and attaches a check-host.net report.
A companion graphic shows the site’s landing page, which advertises a Saudi eVisa processed before travel, beside a red server down icon. A browser capture displays a Cloudflare page stating that the SSL handshake failed. Two uptime checker captures show the site reachable first and then down for everyone.
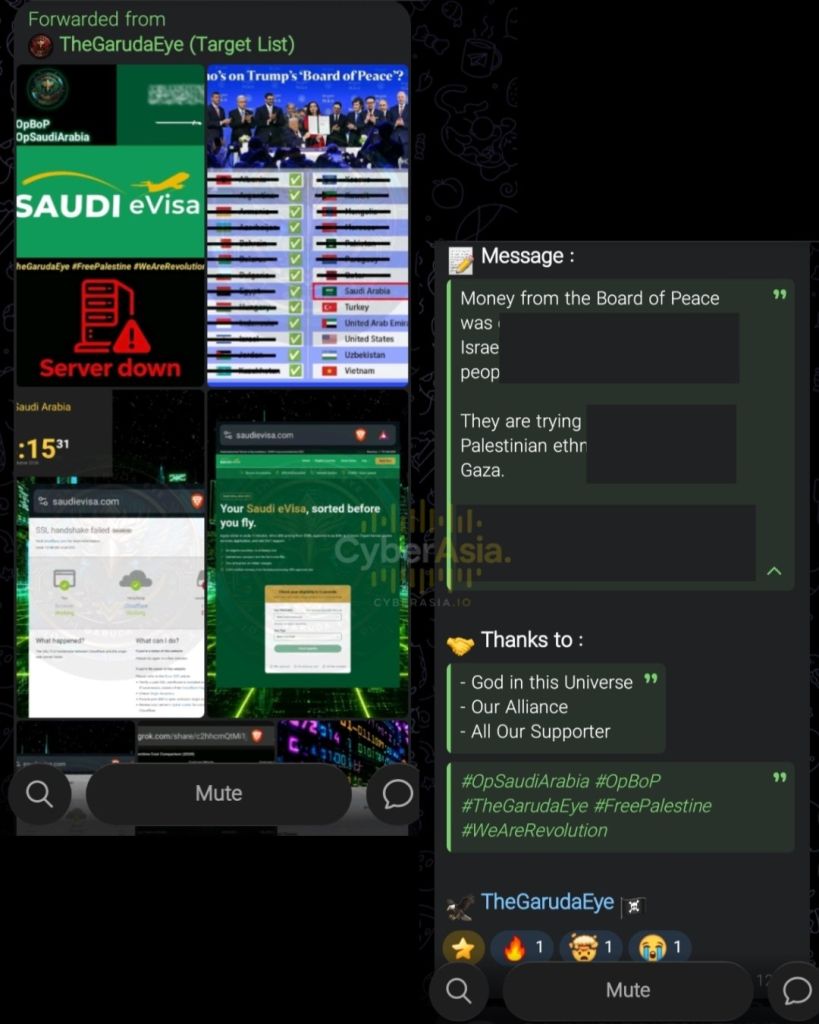
A handshake failure at the Cloudflare layer fits an origin server too busy to complete secure connections. Visitors would have met an error page instead of the application form. The captures show no data theft and no access to applicant records.
Attack #0139: Saudi Water Authority Returns Error 522 and 503
The second announcement lists Saudi Arabia Government and the Saudi Water Authority (SWA), with swa.gov.sa named in the post. It gives 08:00 AM Saudi time on 9 October 2026 as the start and offers two check-host reports.
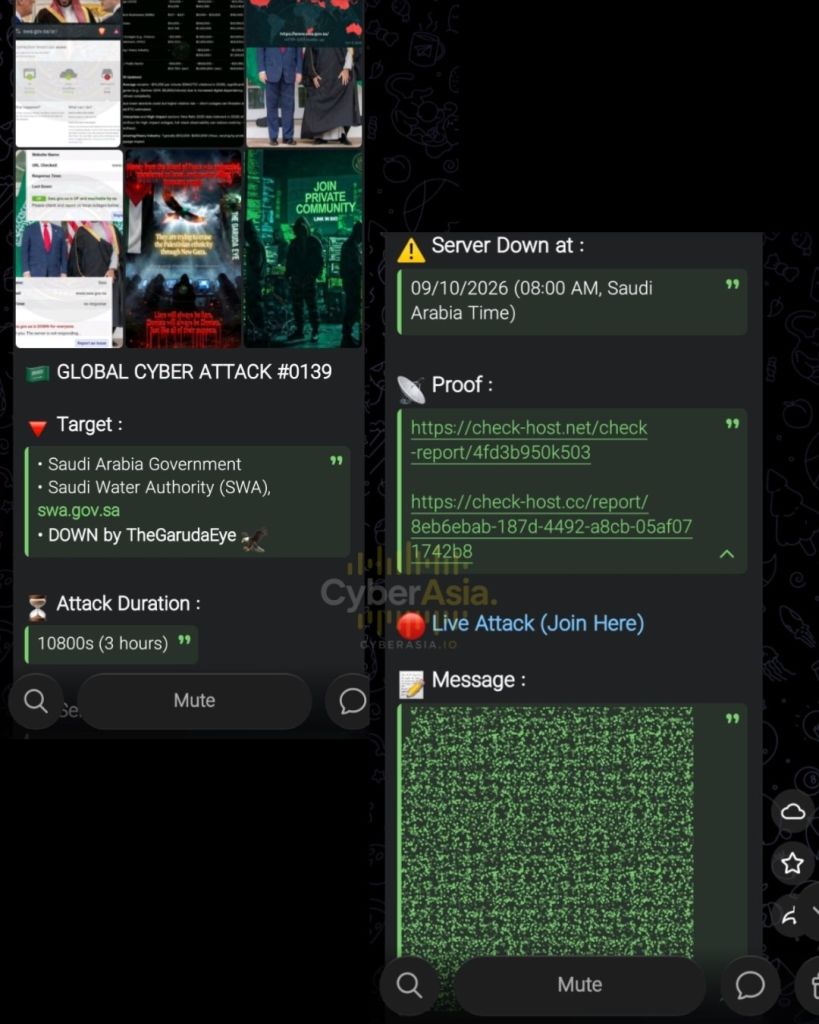
The strongest capture shows the Arabic page swa.gov.sa/ar/ returning a Cloudflare Connection timed out page with error code 522. A Saudi Arabia clock in the same image reads 08:00:49 on Friday, 9 October 2026, and the page timestamp of 2026-10-09 05:01:06 UTC converts to 08:01 AM Saudi time. The browser and the Riyadh Cloudflare edge are marked working, while only the host at www.swa.gov.sa shows an error.
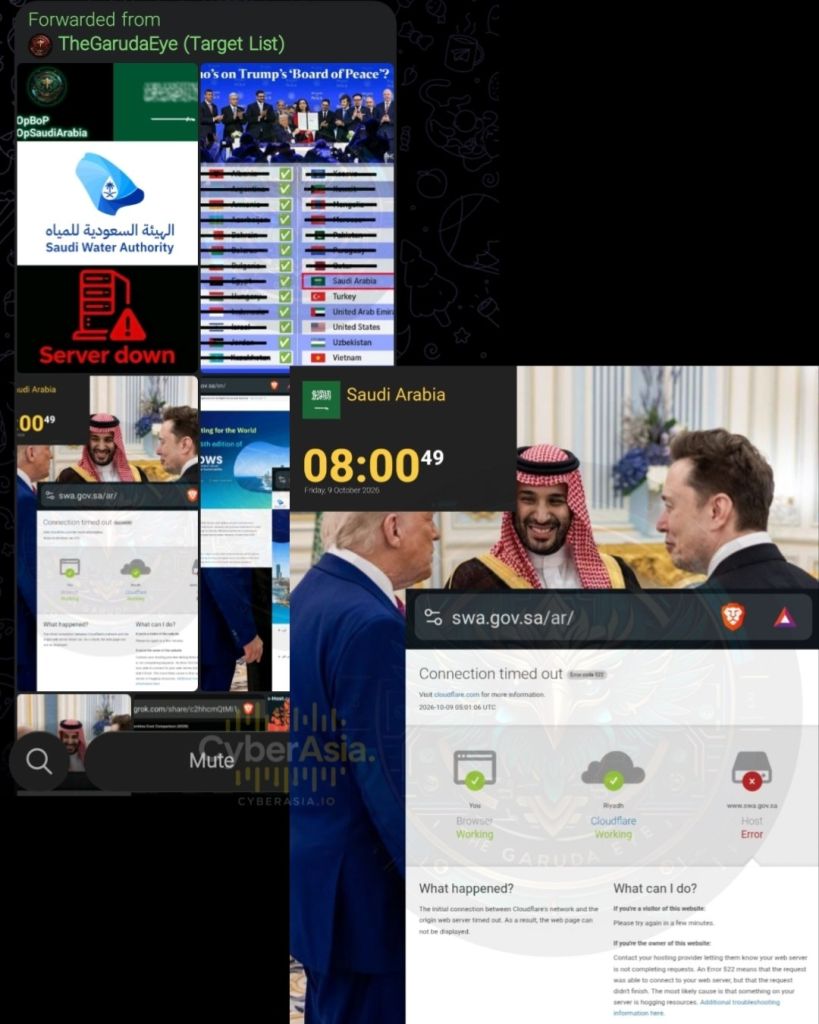
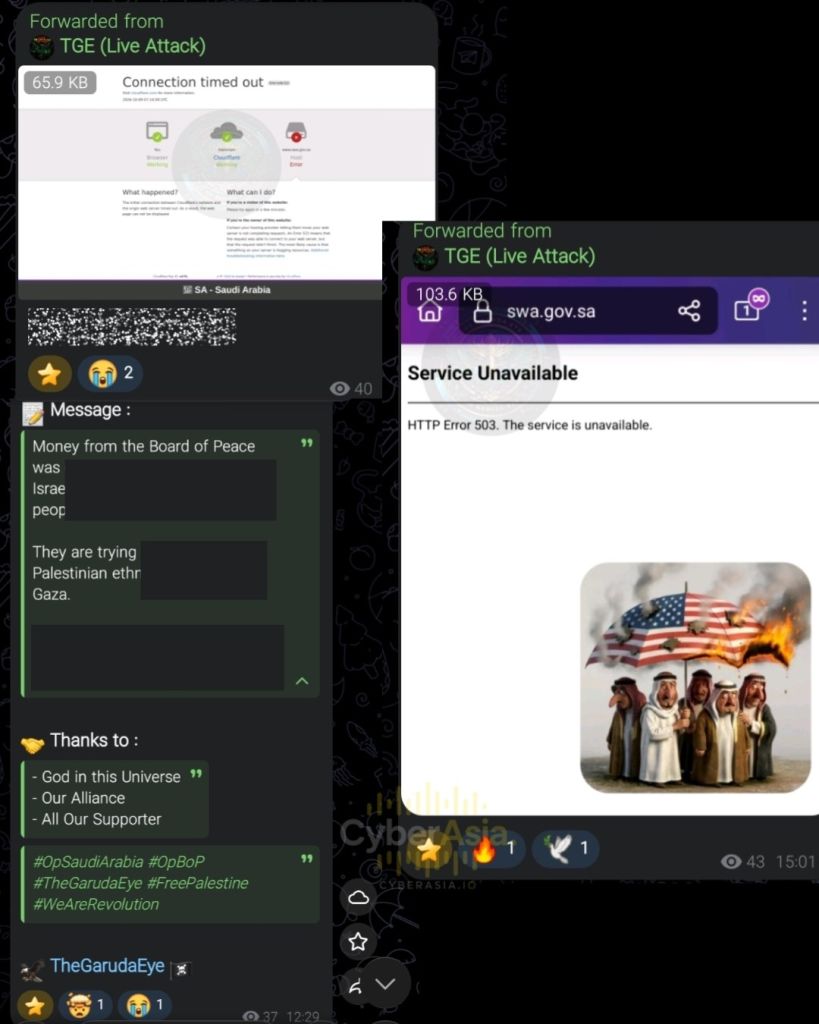
Posts forwarded from a feed the group labels TGE (Live Attack) repeat the 522 page, then show a mobile browser capture of swa.gov.sa returning HTTP Error 503, Service Unavailable. That capture is paired with a political cartoon of a burning American flag used as an umbrella, which says more about the campaign’s messaging than its method.
What the Error Codes Suggest About the Attack Method
Cloudflare’s documentation explains that Error 522 appears when the origin web server fails to answer Cloudflare’s connection request in time. Common causes include an overloaded or offline origin and dropped packets.
Here the edge network stayed online while the origin stopped answering. That pattern usually means traffic reaching the origin was heavy enough to exhaust it, and the 503 response points the same way. The group has not published its method. A Layer 7 HTTP flood is a common candidate for this kind of TheGarudaEye DDoS outage, but nothing in the screenshots confirms it.
The evidence has limits. The captures document each outage start, so the three hour duration rests on the group’s post. Check-host reports show reachability from several probe locations, which helps with timing but not attribution. No screenshot points to a breach, and nothing connects the SWA incident to water treatment or distribution systems. A DDoS attack targets the availability of a public website, not the operational technology behind it.
OpSaudiArabia and OpBoP: The Message Behind the Outages
TheGarudaEye DDoS posts carry the tags #OpSaudiArabia, #OpBoP, #TheGarudaEye, #FreePalestine, and #WeAreRevolution. One graphic lists countries associated with the Board of Peace and outlines Saudi Arabia in a red box.
The Board of Peace was launched by US President Donald Trump around the Gaza ceasefire plan. In January 2026, Saudi Arabia, Turkey, Egypt, Jordan, Indonesia, Pakistan, Qatar, and the United Arab Emirates announced they would join, according to Al Jazeera.
The message block is partly obscured in the screenshots. The visible text links the operation to money associated with the Board of Peace and refers to Palestinians in Gaza.
The emblem shows a Garuda head with a gold crest and green wings inside a ring of circuit board patterns. The material reviewed does not disclose where the group operates or who belongs to it
How Admins Can Reduce DDoS Downtime
Any site behind a CDN can face the same 522 and 503 sequence if its origin is reachable and weakly protected. Admins can start here:
- Restrict the origin firewall to the CDN’s published address ranges.
- Cache static and semi-static pages so repeat requests never reach the origin.
- Rate limit expensive endpoints such as search and form pages.
- Run uptime checks from several regions every minute and alert on 522 and 503 spikes.
For a related case with the same error pattern, see RipperSec DDoS attack on Israeli retailer BUG.
FAQ
Q1 : Were saudievisa.com and swa.gov.sa hacked or only knocked offline?
The evidence shows loss of availability only. The screenshots contain error pages and outage reports, with no leaked files or admin panel access.
Q2 : Did the Saudi Water Authority outage affect water supply?
Nothing in the material points to that. The affected property is the public website, and the screenshots show no link to treatment or distribution systems.
Q3 : What does Cloudflare Error 522 mean for a website owner?
Cloudflare reached its own edge but could not complete a connection to the origin server in time. Owners should check origin load, firewall rules, and whether the origin address in DNS is current.
Q4 : Is it safe to apply for a Saudi eVisa after an outage like this?
Use the official government platform at visa.visitsaudi.com and confirm the web address before entering passport details. If a page is slow, wait and retry instead of switching to unfamiliar lookalike sites.
Research Notice
This article is published for cybersecurity awareness and research. CyberAsia.io reports publicly posted material and does not support, endorse, or encourage attacks on any organization.
Disclaimer: The information presented in this threat intelligence report is for educational and cybersecurity research purposes only. CyberAsia reports on cyber incidents to help organizations understand and defend against emerging threats. We do not provide hacking instructions, host stolen data, or endorse illegal activities.
> INTELLIGENCE_NOTICE
The report above detailing TheGarudaEye DDoS Hits Saudi eVisa, SWA: 2 Critical Outages is part of the CyberAsia public archive. For organizations requiring real-time attack telemetry, check-host latency records, and edge firewall mitigation strategies for ddos incidents, please refer to our Secure Drop or contact the research desk.