 ddos
ddos
313 Team Announces Saudi Civil Defense Official Site Is Down
> By Clara | Oct 06, 2026 | 6 min read
The official website of Saudi Arabia’s General Directorate of Civil Defense, 998.gov.sa, failed to respond from more than 30 monitoring points across multiple countries on Tuesday, September 15, 2026. 313 Team, a group that calls itself the Islamic Cyber Resistance in Iraq, attached the test results to an announcement that it had attacked the agency’s servers.
Every row of the check-host.net report shows the same result: Connection timed out. The time and HTTP code columns are empty, meaning the server returned no response at all. The test was logged at 15:48 UTC.
The agency, which operates under Saudi Arabia’s Ministry of Interior, handles firefighting, rescue, and national emergency management. Its domain name is derived from the agency’s emergency service number, 998.
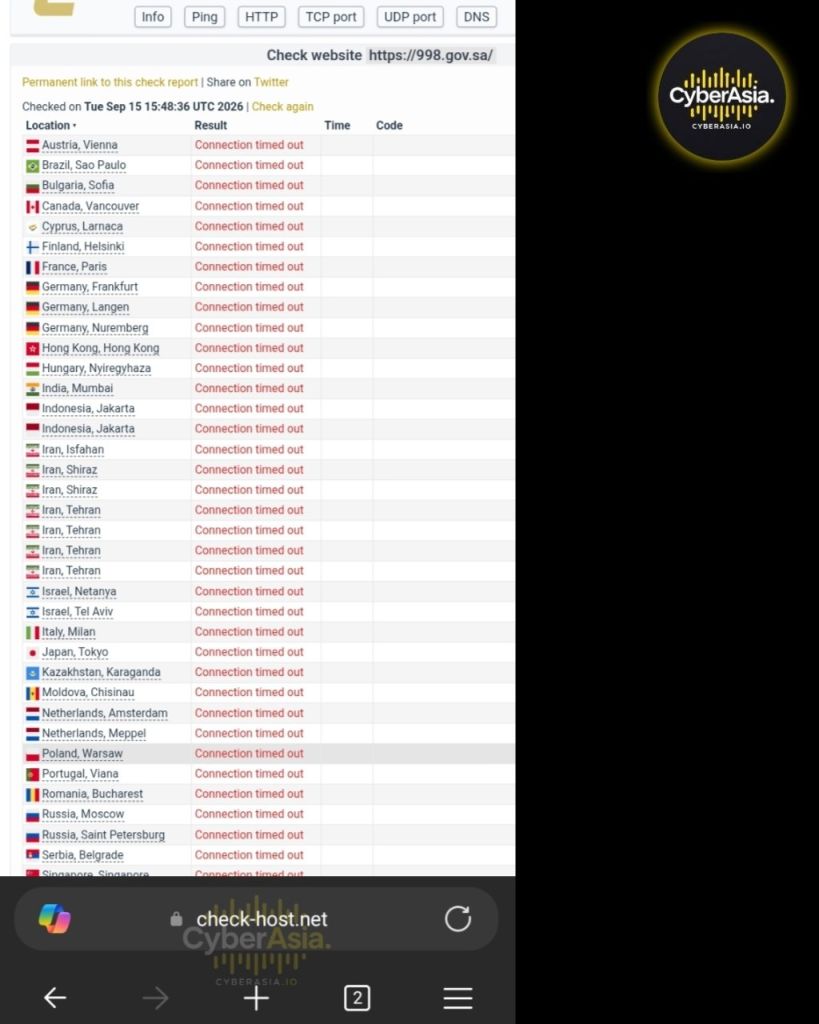
check-host.net Test Results: Timeouts at More Than 30 Locations
The report shared by 313 Team uses an HTTP test against the address https://998.gov.sa/. The monitoring points visible in the screenshot include Vienna, São Paulo, Frankfurt, Paris, Moscow, Mumbai, Tokyo, Tel Aviv, Tehran, and two points in Jakarta. All of them logged timeouts, so the disruption was also visible from Indonesia.
A result like this is different from a 502 or 504 error. Those codes indicate that an intermediary server is still answering the client and has only failed to pass the request on to the server behind it. In this report there is no response of any kind, so the code column is left blank.
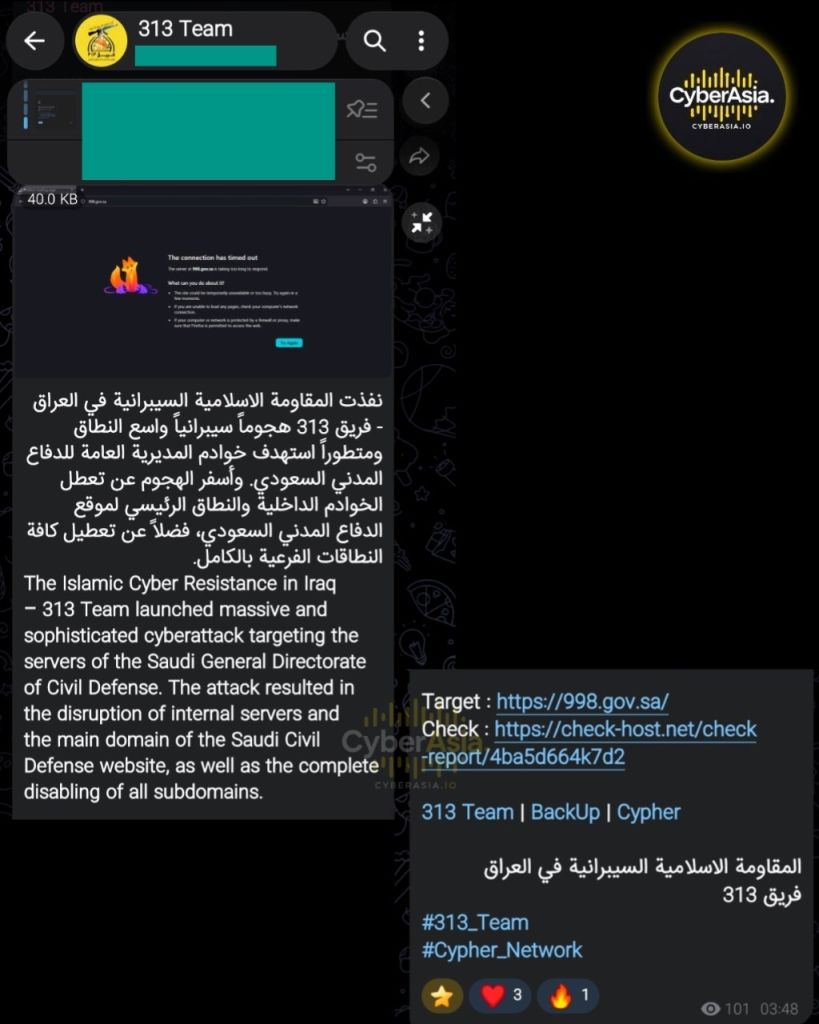
313 Team also attached a browser screenshot with a message saying the 998.gov.sa server took too long to respond. The image carries no timestamp.
313 Team’s Statement and the Subdomain List
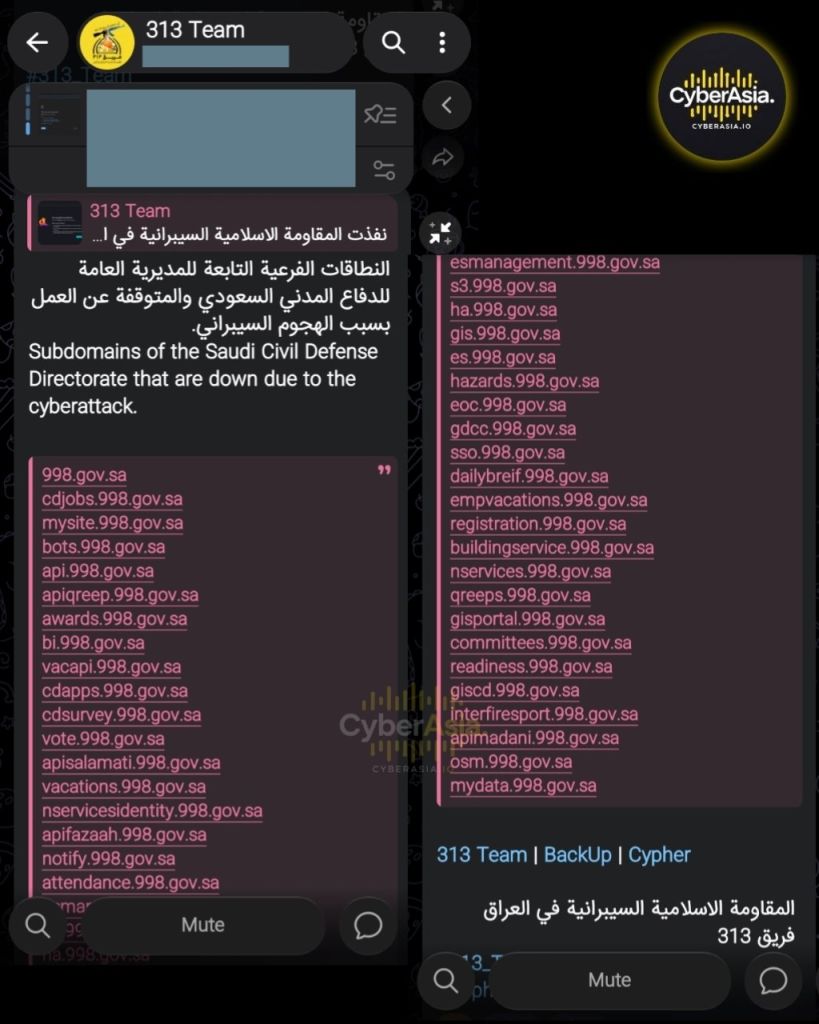
313 Team’s announcement was written in Arabic and English. The group described its attack as large-scale and sophisticated, aimed at the servers of the Saudi General Directorate of Civil Defense. The result, according to the group, was disruption of internal servers and the main domain, followed by a complete shutdown of all subdomains.
The message lists the target and a link to the check-host.net report, then closes with the sign-off tags 313 Team, BackUp, and Cypher, along with the hashtags #313_Team and #Cypher_Network. It mentions no motive, demand, or attack vector, such as a Layer 7 HTTP flood or UDP reflection.
A follow-up message contains a list of subdomains that it says also went offline. There are about 40 of them, not counting the main domain. Judging by their names, the subdomains appear to serve recruitment (cdjobs), employee leave (vacations and empvacations), registration (registration), building services (buildingservice), geographic information systems (gis and gisportal), the emergency operations center (eoc), and single sign-on (sso). Several entries begin with api, a naming convention commonly used for interfaces that connect systems to one another.
The list comes from 313 Team’s own message. The available screenshots contain no separate tests for individual subdomains, only for the main domain.
313 Team’s Track Record Against Saudi Targets
Cyble describes 313 Team as a pro-Iran hacktivist collective whose most prominent capability is distributed denial-of-service (DDoS) attacks. Researchers have recorded Iraq, Spain, Saudi Arabia, and the United States among the countries it has targeted.
Saudi Arabia is not new territory for the group. Hackmanac recorded nine Saudi targets named by 313 Team in August 2025, including Absher, the Ministry of Commerce, and the Saudi Press Agency. VECERT logged a statement from the group about Nafath, the national identity platform, on July 13, 2026. Two days before the test on 998.gov.sa, the same tracker logged a similar statement against Saudi National Bank, complete with a check-host.net link.
FalconFeeds identifies March 2026 as the group’s most intense period, with a 72-hour DDoS campaign against 15 Kuwaiti institutions and website defacement in the Saudi health sector.
Its playbook is a familiar one. Graphika noted that during attacks on Bluesky and eBay in April 2026, 313 Team shared screenshots of outage reports to attract attention. Intel 471 says check-host.net links have become the standard way for the hacktivist community to show the results of their attacks, especially since activity surged after the United States and Israel struck Iran on February 28, 2026.
Read also: https://cyberasia.io/actor/313-team/
Limits of the Evidence and Impact on Civil Defense Services
A check-host.net report captures only a single moment. It shows that 998.gov.sa did not respond at 15:48 UTC, but it does not show who caused the outage or how long it lasted.
The tool cannot tell a traffic surge apart from region-based access restrictions, which some government websites in various countries apply, or from system maintenance. The monitoring points visible in the screenshot also include no location inside Saudi Arabia, so it is unclear whether users there experienced the same thing.
As of this writing, our editorial team has not found a public statement about the disruption from the General Directorate of Civil Defense or Saudi Arabia’s Ministry of Interior. The screenshots also do not show whether the site has recovered.
As for the impact, 313 Team’s message addresses only the website and its subdomains. According to Saudipedia, emergency reports are received through the number 998 in most provinces, while the Riyadh and Makkah regions use 911 through the Unified Security Operations Center. Nothing in the group’s material mentions any disruption to those phone lines.
FAQ: Questions About the 998.gov.sa Outage
Q1 : Was personal data of citizens or Civil Defense personnel leaked?
The available material does not mention any theft or release of data. All that has been reported is a website and subdomains that could not be reached. A DDoS attack works by flooding a server so that it cannot serve requests, not by opening a database. Suspicion of a leak would only have a basis once data samples or evidence of an intrusion appear.
Q2 : How can dozens of subdomains go down at the same time?
Subdomains that share the same IP address, application gateway, or DNS service can go down together if that shared point is overwhelmed. The available material does not make it possible to confirm whether that is what happened here.
Q3 : How do you read check-host.net results correctly?
Look at three things: the type of test used (HTTP, ping, or TCP), the spread of locations, and the time of the test. Timeouts from one or two locations may come from local network problems, while timeouts from dozens of locations in many countries point to the server side. Rerun the test several times to see whether the disruption is still ongoing.
Q4 : What emergency containment steps should system administrators take?
- Contact the hosting provider or internet service provider (ISP), then enable a scrubbing service or content delivery network (CDN) to absorb the excess traffic.
- Apply rate limiting and web application firewall (WAF) rules against abnormal HTTP requests.
- Separate core services such as the API and SSO from the public website, then serve a static fallback page.
- Keep traffic logs and firewall records for analysis and incident reporting.
Disclaimer: The information presented in this threat intelligence report is for educational and cybersecurity research purposes only. CyberAsia reports on cyber incidents to help organizations understand and defend against emerging threats. We do not provide hacking instructions, host stolen data, or endorse illegal activities.
> INTELLIGENCE_NOTICE
The report above detailing 313 Team Announces Saudi Civil Defense Official Site Is Down is part of the CyberAsia public archive. For organizations requiring real-time attack telemetry, check-host latency records, and edge firewall mitigation strategies for ddos incidents, please refer to our Secure Drop or contact the research desk.