Attribution
Iran (IRGC-Linked)
Motivation
Hacktivism, Religious, Anti-Israel
Modus Operandi (MO)
Web defacement, DDoS, data leaks targeting Israeli and Western entities
Primary Aliases
313 Hacking Team
313 Team is an Iranian hacktivist group whose name is a reference to the Islamic theological concept that 313 warriors will accompany the Mahdi (the Islamic messiah figure) during the end times. The group is assessed to be affiliated with or sympathetic to the Islamic Revolutionary Guard Corps (IRGC) and operates in alignment with broader Iranian geopolitical objectives.
The group primarily targets Israeli and Western organisations through web defacement, DDoS attacks, and data theft operations. Their campaigns are often timed to coincide with significant dates in the Islamic calendar or in response to geopolitical events in the Middle East, suggesting coordination with broader Iranian information operations.
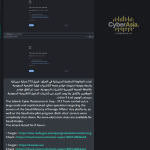
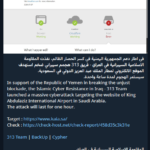
313 Team has publicly claimed successful intrusions against Israeli financial institutions, military contractor websites, and government portals. While some claims have been independently verified, others appear exaggerated for psychological and propaganda effect.
The group maintains an active Telegram channel and social media presence, using these platforms to publish evidence of attacks, recruit new members, and coordinate with allied hacktivist organisations across the Middle East and beyond.
Historical Operations & TTP Evolution
Analysis of historical telemetry associated with this threat actor reveals a highly adaptive operational tempo. Initial campaigns were characterized by opportunistic exploitation of known vulnerabilities (N-days) in perimeter-facing infrastructure. However, recent forensic investigations indicate a significant evolution in their Tactics, Techniques, and Procedures (TTPs). The group has increasingly integrated sophisticated defense evasion mechanisms, utilizing bespoke malware droppers and "Living off the Land" (LotL) binaries to bypass traditional endpoint detection systems.
Target Demographics & Strategic Motivations
The targeting profile of this collective has expanded considerably over the past year. While initial operations primarily focused on opportunistic financial extortion within the SME sector, current intelligence suggests a strategic pivot towards high-value targets within critical infrastructure, government logistics, and regional financial institutions. This shift implies an alignment with broader geopolitical objectives or the acquisition of more advanced Initial Access Broker (IAB) networks.
Recommended Mitigation & Defensive Posture
To defend against the specific methodologies employed by this actor, organizations must prioritize the following mitigation strategies:
- Strict Network Segmentation: Enforce the Purdue Model for OT environments and strict VLAN segmentation for IT networks to prevent lateral movement following a perimeter breach.
- Behavioral EDR Deployment: Traditional signature-based antivirus is ineffective against their LotL tactics. Deploy advanced Endpoint Detection and Response (EDR) solutions configured for behavioral anomaly detection.
- Continuous Identity Verification: Mandate phishing-resistant Multi-Factor Authentication (MFA) across all administrative accounts, VPNs, and remote access gateways to neutralize credential stuffing attacks.
- Proactive Threat Hunting: Integrate associated Indicators of Compromise (IoCs) and YARA rules into automated Threat Intelligence Platforms (TIPs) for continuous monitoring.
Note: This dossier is continuously updated as new intelligence regarding the actor's operations becomes available. Analysts are advised to monitor associated C2 infrastructure for shifts in targeting priorities.