 ddos
ddos
Meitav DDoS: RipperSec’s Shocking Strike Exposed in 7 Posts
> By Clara | Oct 12, 2026 | 6 min read
The Meitav DDoS attack pushed meitav.co.il, the public website of one of Israel’s largest investment houses, into repeated timeouts on 9 September 2026. RipperSec, the pro-Palestinian hacktivist group behind the #OpZionistV2 campaign, documented the strike in seven posts timestamped between 21:00 and 22:10.
The screenshots reviewed by CyberAsia.io draw a mixed picture. Many probe locations report timed-out or reset connections, a few still return HTTP 200, and one phone capture ends on an empty browser page. What the posts cannot show is whether trading or fund systems behind the website were touched.
> TABLE_OF_CONTENTS [toggle]
- > Meitav DDoS Attack Timeline: From Target Release to Final Report
- > What the Meitav DDoS Evidence Shows: Timeouts, Resets and an Empty PageMegaMedusa Logs and the Red Map (21:18 and 21:19)
- > Before and After on the Homepage (21:44 and 21:45)
- > Later Checks at 21:59 and 22:10
- > Reading the Numbers: Partial Outage, Not a Total Blackout
- > RipperSec and MegaMedusa: Who Is Behind the Traffic
- > Why Meitav Matters
- > FAQ
- > Educational Research Notice
Meitav DDoS Attack Timeline: From Target Release to Final Report
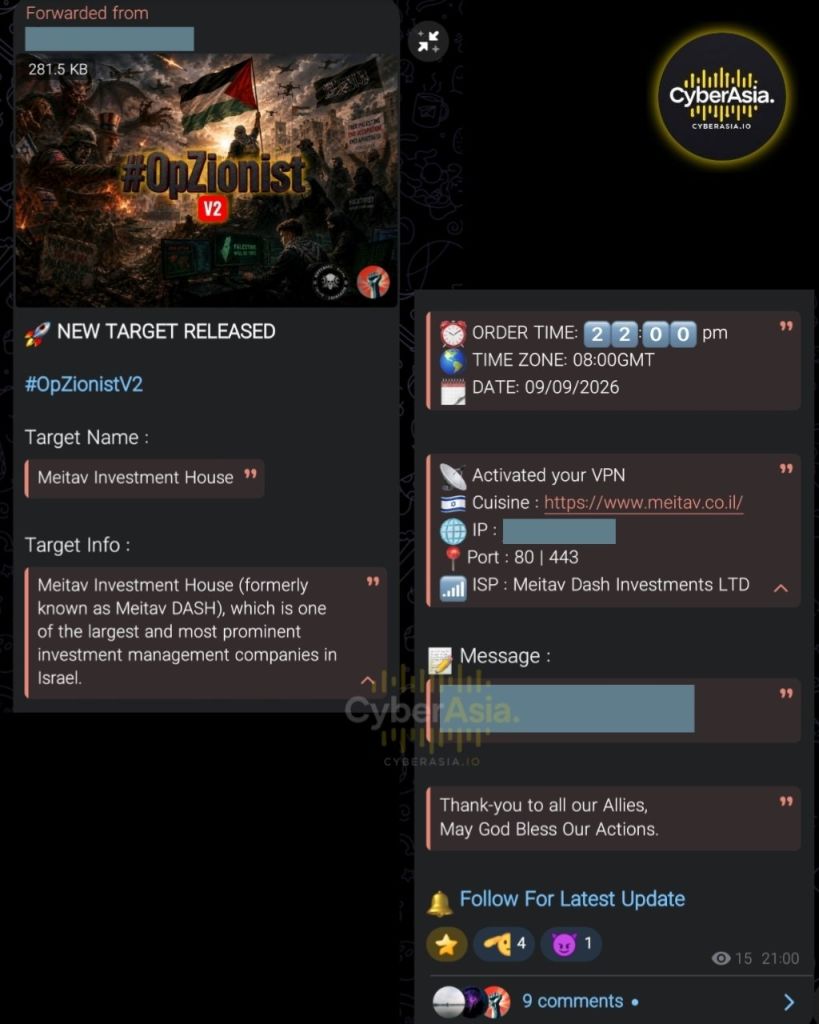
The sequence opens at 21:00 with a post headed NEW TARGET RELEASED. It names Meitav Investment House, formerly Meitav DASH, as the objective of #OpZionistV2 and lists the address https://www.meitav.co.il/, ports 80 and 443, and Meitav Dash Investments LTD as the ISP.
An order time follows: 22:00 on 09/09/2026, with the time zone written as 08:00 GMT, most likely GMT+8. The post closes with thanks to allies and an invitation to follow the channel for updates.
The rest of the Meitav DDoS timeline is six posts between 21:18 and 22:10, each pairing a terminal capture or browser view with a check-host link. The same tag appeared on 4 September against TV7 Israel News, covered in https://cyberasia.io/article/ddos/ddos-rippersec-tv7-israel-news/: CyberAsia.io report on RipperSec’s DDoS against TV7 Israel News].
What the Meitav DDoS Evidence Shows: Timeouts, Resets and an Empty PageMegaMedusa Logs and the Red Map (21:18 and 21:19)
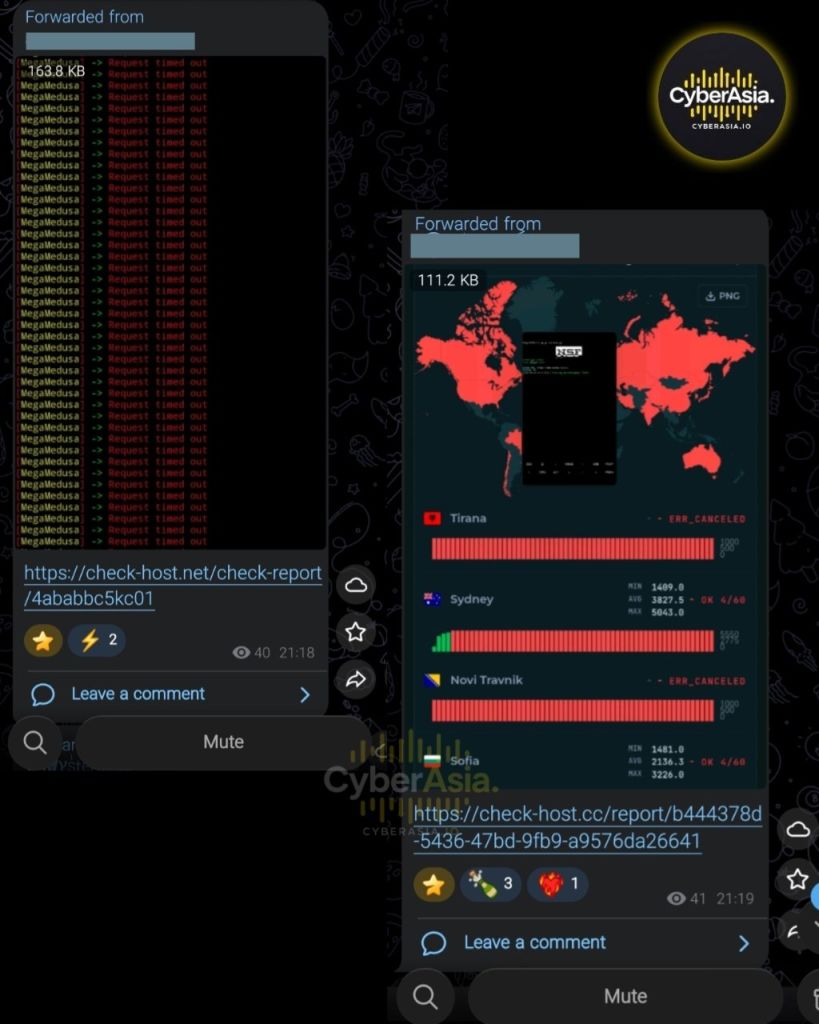
The first evidence post is a long terminal capture where every visible line reads Request timed out, each tagged MegaMedusa. A minute later comes a check-host.cc report with a world map painted red. Tirana in Albania and Novi Travnik in Bosnia and Herzegovina return ERR_CANCELED with no successful request.
Two other rows carry hard numbers. Sydney succeeded on only 4 of 60 requests, averaging 3,827.5 ms with a peak of 5,043 ms. Sofia also managed 4 of 60, averaging 2,136.3 ms. For a corporate homepage, that is slow and mostly failing.
Before and After on the Homepage (21:44 and 21:45)
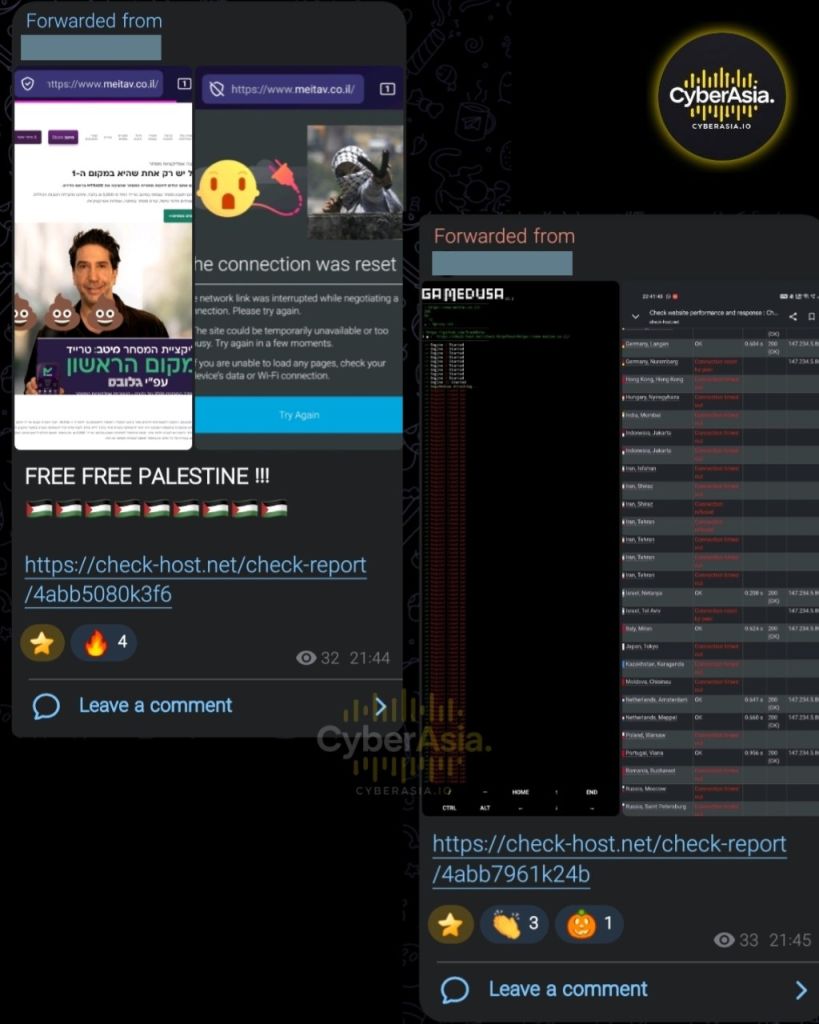
At 21:44 the group posted a split capture of meitav.co.il. On the left, the Hebrew-language homepage loads with a promotional banner. On the right, the browser stops at a page reading “The connection was reset.”
One minute later, a second post shows the MegaMedusa banner and a check-host table. Timeouts fill the rows for Hong Kong, Mumbai, Jakarta, Tokyo, Moscow and several Iranian cities, and Tel Aviv returns a connection reset. Only a handful of nodes still answer HTTP 200 in under a second: Langen, Netanya, Milan, Amsterdam, Meppel and Viana.
Later Checks at 21:59 and 22:10
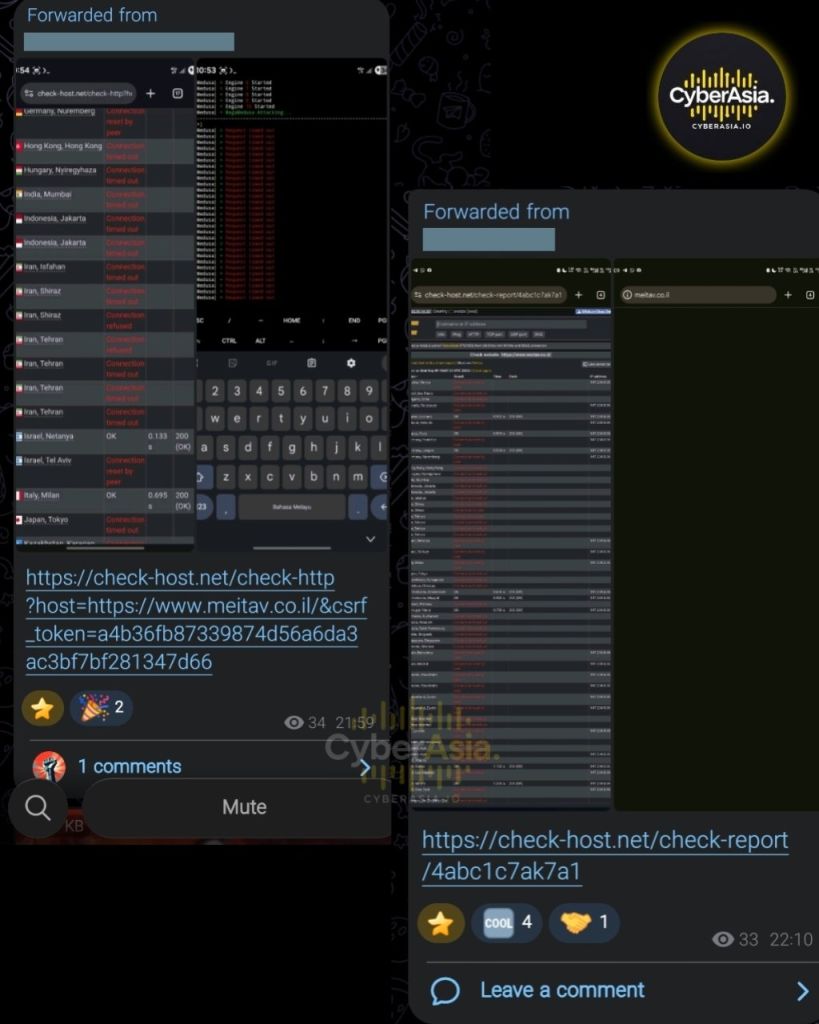
The 21:59 post links a check-host HTTP test aimed at www.meitav.co.il, beside a phone terminal reading MegaMedusa Attacking. Netanya and Milan still answer HTTP 200. The 22:10 post, the last in the series, shows the same pattern plus a browser tab on meitav.co.il with nothing on the page.
Reading the Numbers: Partial Outage, Not a Total Blackout
The Meitav DDoS evidence supports a narrow conclusion. The homepage failed from many vantage points, yet never everywhere at once. Nodes in Germany, the Netherlands, Italy, Portugal and Israel answered HTTP 200 in the 21:45 report, and Netanya and Milan did so again at 21:59.
None of the visible rows shows a 502, 504 or 429. Every failure is connection-level: timed out, reset by peer, refused or canceled. That fits a flood that saturates the front end before the application can reply. The listed ports, 80 and 443, and the MegaMedusa label point to an application-layer HTTP flood rather than UDP reflection.
Two cautions apply. Probes from Iran, Russia and Kazakhstan can fail on Israeli sites through geo-filtering alone, so those rows prove little. And each report is a snapshot chosen by the group, so nothing here measures how long the disruption lasted.
RipperSec and MegaMedusa: Who Is Behind the Traffic
Radware describes RipperSec as a pro-Palestinian hacktivist group, and MegaMedusa as a public Layer 7 DDoS tool maintained by one of its members. Cyble’s profile attributes nearly 200 DDoS attacks to the group, many aimed at Israeli government and private-sector sites.
The screenshots behind this Meitav DDoS report fit that profile. The terminal captures show the MegaMedusa name, and the phone keyboard. Because the tool is public, volunteers can join an announced operation with modest technical skill.
Why Meitav Matters
Meitav Investment House trades on the Tel Aviv Stock Exchange under the ticker MTAV. A company release dated 31 August 2026, which refers readers to its investor relations page, puts assets under management at about NIS 467.5 billion for more than 1.6 million clients as of July.
A Meitav DDoS outage at that scale lands on customer service first. Visitors cannot reach information pages, and call centers absorb the overflow. A homepage flood does not by itself touch pension or fund systems, and nothing in the posts suggests it did.
FAQ
Q1. Did the Meitav DDoS attack leak customer data?
Nothing in the posts shows data theft. A DDoS floods a website with requests to slow it or knock it offline, and it does not require database access. The ports named in the target post are standard web ports.
Q2. Why do some check-host nodes show OK while others time out?
Each node tests from a different network. Routing, caching, rate limits and country filters can leave one region unreachable while another gets through, and a report captures only a single moment.
Q3. How can I tell whether a site is down for everyone or only for me?
Run the address through check-host.net and compare several countries. If nodes near you fail while others respond, the problem may be regional, though country filters can block some locations on a normal day.
Q4. What should an affected IT team do first?
Call the ISP or CDN provider and ask for upstream filtering. Turn on rate limits and bot challenges, serve a static fallback for the homepage, and keep full logs. The CISA, FBI and MS-ISAC joint guide covers these steps in detail.
Educational Research Notice
This report is published for cybersecurity education and awareness. CyberAsia.io does not endorse or assist any attack, and readers must not attempt to reproduce the activity described here. The analysis of the Meitav DDoS attack rests on screenshots and links that RipperSec published. This report will be updated if Meitav Investment House or Israeli authorities release an incident statement.
Disclaimer: The information presented in this threat intelligence report is for educational and cybersecurity research purposes only. CyberAsia reports on cyber incidents to help organizations understand and defend against emerging threats. We do not provide hacking instructions, host stolen data, or endorse illegal activities.
> INTELLIGENCE_NOTICE
The report above detailing Meitav DDoS: RipperSec’s Shocking Strike Exposed in 7 Posts is part of the CyberAsia public archive. For organizations requiring real-time attack telemetry, check-host latency records, and edge firewall mitigation strategies for ddos incidents, please refer to our Secure Drop or contact the research desk.